CWE-22
Allowed-with-ReviewImproper Limitation of a Pathname to a Restricted Directory ('Path Traversal')
Abstraction: Base · Status: Stable
The product uses external input to construct a pathname that is intended to identify a file or directory that is located underneath a restricted parent directory, but the product does not properly neutralize special elements within the pathname that can cause the pathname to resolve to a location that is outside of the restricted directory.
15153 vulnerabilities reference this CWE, most recent first.
GHSA-MMFC-28M2-824Q
Vulnerability from github – Published: 2022-05-14 02:37 – Updated: 2022-05-14 02:37Atlassian Bitbucket Server before 4.7.1 allows remote attackers to read the first line of an arbitrary file via a directory traversal attack on the pull requests resource.
{
  "affected": [],
  "aliases": [
    "CVE-2016-4320"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-22"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2017-04-10T03:59:00Z",
    "severity": "MODERATE"
  },
  "details": "Atlassian Bitbucket Server before 4.7.1 allows remote attackers to read the first line of an arbitrary file via a directory traversal attack on the pull requests resource.",
  "id": "GHSA-mmfc-28m2-824q",
  "modified": "2022-05-14T02:37:09Z",
  "published": "2022-05-14T02:37:09Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2016-4320"
    },
    {
      "type": "WEB",
      "url": "https://confluence.atlassian.com/bitbucketserver/bitbucket-server-4-7-release-notes-829052416.html"
    },
    {
      "type": "WEB",
      "url": "https://jira.atlassian.com/browse/BSERV-8819"
    },
    {
      "type": "WEB",
      "url": "http://www.securityfocus.com/bid/97515"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:N/A:N",
      "type": "CVSS_V3"
    }
  ]
}
GHSA-MMG6-4QMV-6PC8
Vulnerability from github – Published: 2026-09-08 18:14 – Updated: 2026-09-08 18:14Impact
Path traversal via link following in the Infracost config-template parser. The readFile, pathExists, isDir, and matchPaths template functions confined repo-supplied paths with a lexical filepath.Rel check plus a leaf-only os.Lstat:
{{ readFile "evil/file" }}
With an intermediate directory symlink committed in the repo (evil -> /), the path is lexically clean and the leaf is a regular file, so both checks pass, but os.ReadFile follows the symlink and reads outside the checkout. The contents are rendered into the generated config and surfaced via the Infracost dashboard and PR comment, so anyone who can open a pull request can read files off the runner.
Affects infracost up to and including v0.10.44. Successful exploitation reads any file the CLI process can reach on the runner. Impact depends on what the run exposes: under on: pull_request (the configuration in Infracost's documentation) fork pull requests run without secrets and with a read-only token, so exposure is limited. If Infracost runs under pull_request_target, or is triggered by a same-repository pull request, the read reaches the repository's secrets, enabling secret theft. The patch confines all four functions regardless of trigger.
Patches
Fixed in v0.10.45 (#3586) by routing all four functions through security.IsPathAllowed, which resolves symlinks anywhere in the path before a segment-aware containment check. The same fix landed in config#14 and parser#144.
- Installed via the official script, a package manager, or the latest Docker tag: upgrade to v0.10.45 (or later) to receive the fix.
- Pinned to a specific version or image digest: bump to v0.10.45.
Workarounds
No full fix without upgrading. To limit exposure: run Infracost under on: pull_request rather than pull_request_target, and keep fork pull requests from receiving secrets (the defaults).
{
  "affected": [
    {
      "package": {
        "ecosystem": "Go",
        "name": "github.com/infracost/infracost"
      },
      "ranges": [
        {
          "events": [
            {
              "introduced": "0"
            },
            {
              "fixed": "0.10.45"
            }
          ],
          "type": "ECOSYSTEM"
        }
      ]
    }
  ],
  "aliases": [
    "CVE-2026-71493"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-22",
      "CWE-59"
    ],
    "github_reviewed": true,
    "github_reviewed_at": "2026-09-08T18:14:00Z",
    "nvd_published_at": "2026-08-21T18:16:50Z",
    "severity": "MODERATE"
  },
  "details": "### Impact\n\nPath traversal via link following in the Infracost config-template parser. The `readFile`, `pathExists`, `isDir`, and `matchPaths` template functions confined repo-supplied paths with a lexical `filepath.Rel` check plus a leaf-only `os.Lstat`:\n\n```\n{{ readFile \"evil/file\" }}\n```\n\nWith an intermediate directory symlink committed in the repo (`evil -\u003e /`), the path is lexically clean and the leaf is a regular file, so both checks pass, but `os.ReadFile` follows the symlink and reads outside the checkout. The contents are rendered into the generated config and surfaced via the Infracost dashboard and PR comment, so anyone who can open a pull request can read files off the runner.\n\nAffects `infracost` up to and including `v0.10.44`. Successful exploitation reads any file the CLI process can reach on the runner. Impact depends on what the run exposes: under `on: pull_request` (the configuration in Infracost\u0027s documentation) fork pull requests run without secrets and with a read-only token, so exposure is limited. If Infracost runs under `pull_request_target`, or is triggered by a same-repository pull request, the read reaches the repository\u0027s secrets, enabling secret theft. The patch confines all four functions regardless of trigger.\n\n### Patches\n\nFixed in `v0.10.45` ([#3586](https://github.com/infracost/infracost/pull/3586)) by routing all four functions through `security.IsPathAllowed`, which resolves symlinks anywhere in the path before a segment-aware containment check. The same fix landed in [config#14](https://github.com/infracost/config/pull/14) and [parser#144](https://github.com/infracost/parser/pull/144).\n  - Installed via the official script, a package manager, or the `latest` Docker tag: upgrade to `v0.10.45` (or later) to receive the fix.\n  - Pinned to a specific version or image digest: bump to `v0.10.45`.\n\n### Workarounds\n\nNo full fix without upgrading. To limit exposure: run Infracost under `on: pull_request` rather than `pull_request_target`, and keep fork pull requests from receiving secrets (the defaults).",
  "id": "GHSA-mmg6-4qmv-6pc8",
  "modified": "2026-09-08T18:14:00Z",
  "published": "2026-09-08T18:14:00Z",
  "references": [
    {
      "type": "WEB",
      "url": "https://github.com/infracost/infracost/security/advisories/GHSA-mmg6-4qmv-6pc8"
    },
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2026-71493"
    },
    {
      "type": "WEB",
      "url": "https://github.com/infracost/infracost/pull/3586"
    },
    {
      "type": "WEB",
      "url": "https://github.com/infracost/infracost/commit/4d39331afc0e27752d16d9d91c34583e5e8487fb"
    },
    {
      "type": "PACKAGE",
      "url": "https://github.com/infracost/infracost"
    },
    {
      "type": "WEB",
      "url": "https://github.com/infracost/infracost/releases/tag/v0.10.45"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:4.0/AV:N/AC:L/AT:P/PR:N/UI:A/VC:H/VI:N/VA:N/SC:N/SI:N/SA:N",
      "type": "CVSS_V4"
    }
  ],
  "summary": "Infracost: Arbitrary file read via config-template readFile symlink traversal"
}
GHSA-MMH6-5CPF-2C72
Vulnerability from github – Published: 2024-03-25 19:35 – Updated: 2024-03-26 12:58Summary
There is a Path Traversal vulnerability in Attachments that allows attackers with admin rights to upload malicious files to other locations of the web root.
PoC
-
In settings, the attachment location is vulnerable to path traversal and can be set to e.g ..\hacked
-
When the above is set, attachments files are now uploaded to e.g C:\Apps\XAMPP\htdocs\hacked instead of C:\Apps\XAMPP\htdocs\phpmyfaq\attachments
-
Verify this by uploading an attachment and see that the "hacked" directory is now created in the web root folder with the attachment file inside.
Impact
Attackers can potentially upload malicious files outside the specified directory.
{
"affected": [
{
"package": {
"ecosystem": "Packagist",
"name": "phpmyfaq/phpmyfaq"
},
"ranges": [
{
"events": [
{
"introduced": "3.2.5"
},
{
"fixed": "3.2.6"
}
],
"type": "ECOSYSTEM"
}
],
"versions": [
"3.2.5"
]
}
],
"aliases": [
"CVE-2024-29196"
],
"database_specific": {
"cwe_ids": [
"CWE-22"
],
"github_reviewed": true,
"github_reviewed_at": "2024-03-25T19:35:09Z",
"nvd_published_at": "2024-03-26T03:15:13Z",
"severity": "LOW"
},
"details": "### Summary\nThere is a Path Traversal vulnerability in Attachments that allows attackers with admin rights to upload malicious files to other locations of the web root.\n\n### PoC\n1. In settings, the attachment location is vulnerable to path traversal and can be set to e.g ..\\hacked\n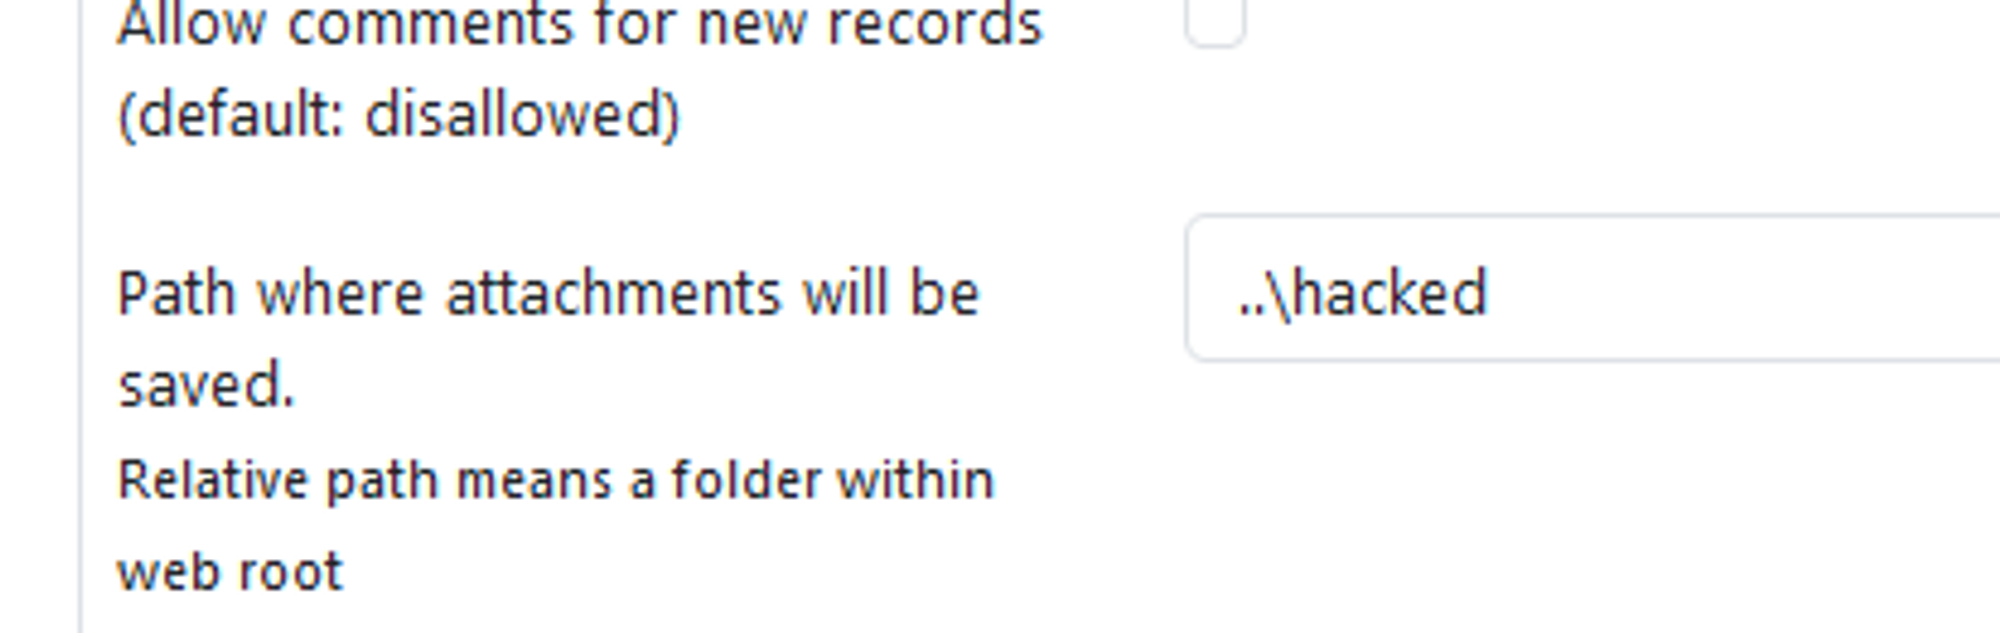\n\n2. When the above is set, attachments files are now uploaded to e.g C:\\Apps\\XAMPP\\htdocs\\hacked instead of C:\\Apps\\XAMPP\\htdocs\\phpmyfaq\\attachments\n\n3. Verify this by uploading an attachment and see that the \"hacked\" directory is now created in the web root folder with the attachment file inside.\n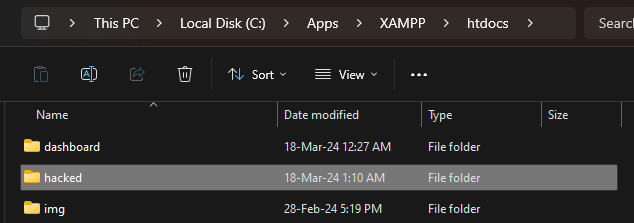\n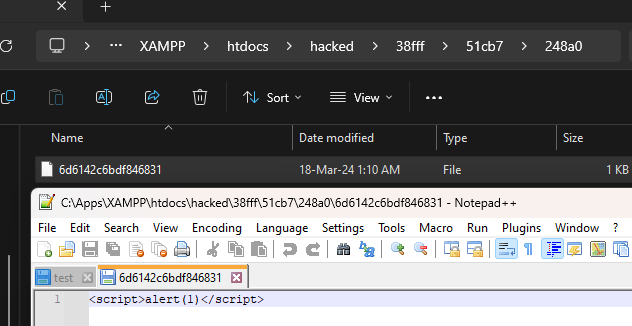\n\n### Impact\nAttackers can potentially upload malicious files outside the specified directory.\n",
"id": "GHSA-mmh6-5cpf-2c72",
"modified": "2024-03-26T12:58:09Z",
"published": "2024-03-25T19:35:09Z",
"references": [
{
"type": "WEB",
"url": "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-mmh6-5cpf-2c72"
},
{
"type": "ADVISORY",
"url": "https://nvd.nist.gov/vuln/detail/CVE-2024-29196"
},
{
"type": "WEB",
"url": "https://github.com/thorsten/phpMyFAQ/commit/7ae2559f079cd5fc9948b6fdfb87581f93840f62"
},
{
"type": "PACKAGE",
"url": "https://github.com/thorsten/phpMyFAQ"
}
],
"schema_version": "1.4.0",
"severity": [
{
"score": "CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:L/I:L/A:N",
"type": "CVSS_V3"
}
],
"summary": "phpMyFAQ Path Traversal in Attachments"
}
GHSA-MMHG-PHMP-2P2V
Vulnerability from github – Published: 2025-07-23 15:31 – Updated: 2025-07-23 15:31A path traversal vulnerability exists in httpdasm version 0.92, a lightweight Windows HTTP server, that allows unauthenticated attackers to read arbitrary files on the host system. By sending a specially crafted GET request containing a sequence of URL-encoded backslashes and directory traversal patterns, an attacker can escape the web root and access sensitive files outside of the intended directory.
{
  "affected": [],
  "aliases": [
    "CVE-2010-10012"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-22"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2025-07-23T14:15:31Z",
    "severity": "HIGH"
  },
  "details": "A path traversal vulnerability exists in httpdasm version 0.92, a lightweight Windows HTTP server, that allows unauthenticated attackers to read arbitrary files on the host system. By sending a specially crafted GET request containing a sequence of URL-encoded backslashes\u00a0and directory traversal patterns, an attacker can escape the web root and access sensitive files outside of the intended directory.",
  "id": "GHSA-mmhg-phmp-2p2v",
  "modified": "2025-07-23T15:31:13Z",
  "published": "2025-07-23T15:31:13Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2010-10012"
    },
    {
      "type": "WEB",
      "url": "https://raw.githubusercontent.com/rapid7/metasploit-framework/master/modules/auxiliary/scanner/http/httpdasm_directory_traversal.rb"
    },
    {
      "type": "WEB",
      "url": "https://www.exploit-db.com/exploits/15861"
    },
    {
      "type": "WEB",
      "url": "https://www.japheth.de/httpdASM.html"
    },
    {
      "type": "WEB",
      "url": "https://www.vulncheck.com/advisories/httpasm-path-traversal"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:H/VI:N/VA:N/SC:N/SI:N/SA:N/E:X/CR:X/IR:X/AR:X/MAV:X/MAC:X/MAT:X/MPR:X/MUI:X/MVC:X/MVI:X/MVA:X/MSC:X/MSI:X/MSA:X/S:X/AU:X/R:X/V:X/RE:X/U:X",
      "type": "CVSS_V4"
    }
  ]
}
GHSA-MMHX-6X77-4JF4
Vulnerability from github – Published: 2022-07-12 00:00 – Updated: 2022-07-16 00:00The Delor4/CarceresBE repository through 1.0 on GitHub allows absolute path traversal because the Flask send_file function is used unsafely.
{
  "affected": [],
  "aliases": [
    "CVE-2022-31515"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-22"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2022-07-11T01:15:00Z",
    "severity": "CRITICAL"
  },
  "details": "The Delor4/CarceresBE repository through 1.0 on GitHub allows absolute path traversal because the Flask send_file function is used unsafely.",
  "id": "GHSA-mmhx-6x77-4jf4",
  "modified": "2022-07-16T00:00:32Z",
  "published": "2022-07-12T00:00:57Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2022-31515"
    },
    {
      "type": "WEB",
      "url": "https://github.com/github/securitylab/issues/669#issuecomment-1117265726"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:C/C:H/I:N/A:L",
      "type": "CVSS_V3"
    }
  ]
}
GHSA-MMJ6-R83C-HQ4F
Vulnerability from github – Published: 2023-06-27 00:30 – Updated: 2024-04-04 05:11A path traversal vulnerability in the Trend Micro Apex One and Apex One as a Service could allow an unauthenticated attacker to upload an arbitrary file to the Management Server which could lead to remote code execution with system privileges.
{
  "affected": [],
  "aliases": [
    "CVE-2023-32557"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-22"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2023-06-26T22:15:10Z",
    "severity": "CRITICAL"
  },
  "details": "A path traversal vulnerability in the Trend Micro Apex One and Apex One as a Service could allow an unauthenticated attacker to upload an arbitrary file to the Management Server which could lead to remote code execution with system privileges.",
  "id": "GHSA-mmj6-r83c-hq4f",
  "modified": "2024-04-04T05:11:29Z",
  "published": "2023-06-27T00:30:24Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2023-32557"
    },
    {
      "type": "WEB",
      "url": "https://success.trendmicro.com/dcx/s/solution/000293108?language=en_US"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H",
      "type": "CVSS_V3"
    }
  ]
}
GHSA-MMM4-X298-C649
Vulnerability from github – Published: 2026-09-14 15:32 – Updated: 2026-09-14 21:31Description
A topology's topology.blobstore.map lets the submitter choose a local name for each blob that the
supervisor localises. That name was used to build a path under the topology's working directory without
normalisation, in both AsyncLocalizer and Container.createBlobstoreLinks, and the symlink helper
force-deletes whatever already exists at the target before creating the link.
A submitter could therefore use ../ segments to direct that delete-and-symlink operation at an arbitrary
path, as the supervisor user, on every node the topology is scheduled onto. The consequences include
recursive deletion of supervisor-owned content and planting a symlink that causes a subsequent worker
launch to execute attacker-chosen code as another tenant's operating-system user, which defeats the
isolation that supervisor.run.worker.as.user is intended to provide.
Mitigation
Upgrade to 3.1.0, where the resolved target must lie inside the expected root at both call sites.
Users who cannot upgrade immediately should restrict topology submission to trusted principals, and may
reject submissions whose topology.blobstore.map entries contain path separators or .. segments before
they reach Nimbus.
Credit
The ASF -- found using Claude agents to study the security of open-source projects, validated and reported by Apache Storm.
{
  "affected": [],
  "aliases": [
    "CVE-2026-82427"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-22"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2026-09-14T15:17:09Z",
    "severity": "HIGH"
  },
  "details": "Description\n\nA topology\u0027s `topology.blobstore.map` lets the submitter choose a local name for each blob that the\nsupervisor localises. That name was used to build a path under the topology\u0027s working directory without\nnormalisation, in both `AsyncLocalizer` and `Container.createBlobstoreLinks`, and the symlink helper\nforce-deletes whatever already exists at the target before creating the link.\n\nA submitter could therefore use `../` segments to direct that delete-and-symlink operation at an arbitrary\npath, as the supervisor user, on every node the topology is scheduled onto. The consequences include\nrecursive deletion of supervisor-owned content and planting a symlink that causes a subsequent worker\nlaunch to execute attacker-chosen code as another tenant\u0027s operating-system user, which defeats the\nisolation that `supervisor.run.worker.as.user` is intended to provide.\n\nMitigation\n\nUpgrade to 3.1.0, where the resolved target must lie inside the expected root at both call sites.\n\nUsers who cannot upgrade immediately should restrict topology submission to trusted principals, and may\nreject submissions whose `topology.blobstore.map` entries contain path separators or `..` segments before\nthey reach Nimbus.\n\nCredit\n\nThe ASF -- found using Claude agents to study the security of open-source projects, validated and reported by Apache Storm.",
  "id": "GHSA-mmm4-x298-c649",
  "modified": "2026-09-14T21:31:38Z",
  "published": "2026-09-14T15:32:48Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2026-82427"
    },
    {
      "type": "WEB",
      "url": "https://lists.apache.org/thread/o0j51w6m0qdmwypvzfnd8w97s7ysnmyj"
    },
    {
      "type": "WEB",
      "url": "http://www.openwall.com/lists/oss-security/2026/09/13/7"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:L/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H",
      "type": "CVSS_V3"
    }
  ]
}
GHSA-MMMG-93RW-WXJF
Vulnerability from github – Published: 2026-02-03 18:30 – Updated: 2026-02-04 18:30Articentgroup Zip Rar Extractor Tool 1.345.93.0 is vulnerable to Directory Traversal. The vulnerability resides in the ZIP file processing component, specifically in the functionality responsible for extracting and handling ZIP archive contents.
{
  "affected": [],
  "aliases": [
    "CVE-2025-63372"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-22"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2026-02-03T18:16:15Z",
    "severity": "HIGH"
  },
  "details": "Articentgroup Zip Rar Extractor Tool 1.345.93.0 is vulnerable to Directory Traversal. The vulnerability resides in the ZIP file processing component, specifically in the functionality responsible for extracting and handling ZIP archive contents.",
  "id": "GHSA-mmmg-93rw-wxjf",
  "modified": "2026-02-04T18:30:30Z",
  "published": "2026-02-03T18:30:46Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2025-63372"
    },
    {
      "type": "WEB",
      "url": "https://articentgroup.com/zip-rar-extractor-tool"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:N/A:N",
      "type": "CVSS_V3"
    }
  ]
}
GHSA-MMPF-X6C4-5PVR
Vulnerability from github – Published: 2022-05-24 16:46 – Updated: 2024-04-04 00:45Adobe XD versions 16.0 and earlier have a path traversal vulnerability. Successful exploitation could lead to arbitrary code execution.
{
  "affected": [],
  "aliases": [
    "CVE-2019-7106"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-22"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2019-05-23T16:29:00Z",
    "severity": "CRITICAL"
  },
  "details": "Adobe XD versions 16.0 and earlier have a path traversal vulnerability. Successful exploitation could lead to arbitrary code execution.",
  "id": "GHSA-mmpf-x6c4-5pvr",
  "modified": "2024-04-04T00:45:51Z",
  "published": "2022-05-24T16:46:29Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2019-7106"
    },
    {
      "type": "WEB",
      "url": "https://helpx.adobe.com/security/products/xd/apsb19-22.html"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H",
      "type": "CVSS_V3"
    }
  ]
}
GHSA-MMQ2-8HQ5-2C6Q
Vulnerability from github – Published: 2026-09-22 09:31 – Updated: 2026-09-22 09:31The Product Feed Manager for WooCommerce – CTX Feed – Support 220+ Shopping & Social Channels plugin for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 6.6.43 via the 'provider' parameter. This makes it possible for authenticated attackers, with shop manager-level access and above, to delete arbitrary files on the server, which can lead to remote code execution when critical files are deleted. Exploitation requires two sequential REST API calls: first to /wp-json/ctxfeed/v1/make_feed/save_feed_config to persist the traversal payload in wp_options, then to /wp-json/ctxfeed/v1/manage_feeds/delete_feed to trigger the unlink(); deletion is further constrained to files whose extensions match the plugin's validated whitelist (csv, xml, tsv, xls, xlsx, json, txt).
{
  "affected": [],
  "aliases": [
    "CVE-2026-15095"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-22"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2026-09-22T09:17:04Z",
    "severity": "MODERATE"
  },
  "details": "The Product Feed Manager for WooCommerce \u2013 CTX Feed \u2013 Support 220+ Shopping \u0026 Social Channels plugin for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 6.6.43 via the \u0027provider\u0027 parameter. This makes it possible for authenticated attackers, with shop manager-level access and above, to delete arbitrary files on the server, which can lead to remote code execution when critical files are deleted. Exploitation requires two sequential REST API calls: first to /wp-json/ctxfeed/v1/make_feed/save_feed_config to persist the traversal payload in wp_options, then to /wp-json/ctxfeed/v1/manage_feeds/delete_feed to trigger the unlink(); deletion is further constrained to files whose extensions match the plugin\u0027s validated whitelist (csv, xml, tsv, xls, xlsx, json, txt).",
  "id": "GHSA-mmq2-8hq5-2c6q",
  "modified": "2026-09-22T09:31:13Z",
  "published": "2026-09-22T09:31:13Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2026-15095"
    },
    {
      "type": "WEB",
      "url": "https://plugins.trac.wordpress.org/browser/webappick-product-feed-for-woocommerce/tags/6.6.38/V5/API/RestController.php#L109"
    },
    {
      "type": "WEB",
      "url": "https://plugins.trac.wordpress.org/browser/webappick-product-feed-for-woocommerce/tags/6.6.38/V5/API/V1/MakeFeed.php#L154"
    },
    {
      "type": "WEB",
      "url": "https://plugins.trac.wordpress.org/browser/webappick-product-feed-for-woocommerce/tags/6.6.38/V5/API/V1/ManageFeeds.php#L378"
    },
    {
      "type": "WEB",
      "url": "https://plugins.trac.wordpress.org/browser/webappick-product-feed-for-woocommerce/tags/6.6.38/V5/Common/Helper.php#L207"
    },
    {
      "type": "WEB",
      "url": "https://plugins.trac.wordpress.org/browser/webappick-product-feed-for-woocommerce/tags/6.6.38/V5/Feed/Feed.php#L113"
    },
    {
      "type": "WEB",
      "url": "https://plugins.trac.wordpress.org/browser/webappick-product-feed-for-woocommerce/tags/6.6.38/V5/Helper/FeedHelper.php#L38"
    },
    {
      "type": "WEB",
      "url": "https://plugins.trac.wordpress.org/changeset?reponame=\u0026old=3627934%40webappick-product-feed-for-woocommerce\u0026new=3627934%40webappick-product-feed-for-woocommerce"
    },
    {
      "type": "WEB",
      "url": "https://www.wordfence.com/threat-intel/vulnerabilities/id/cac5e5ca-34cc-4219-96a3-438c5a1d6a23?source=cve"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:N/A:N",
      "type": "CVSS_V3"
    }
  ]
}
Mitigation MIT-5.1
Strategy: Input Validation
- Assume all input is malicious. Use an "accept known good" input validation strategy, i.e., use a list of acceptable inputs that strictly conform to specifications. Reject any input that does not strictly conform to specifications, or transform it into something that does.
- When performing input validation, consider all potentially relevant properties, including length, type of input, the full range of acceptable values, missing or extra inputs, syntax, consistency across related fields, and conformance to business rules. As an example of business rule logic, "boat" may be syntactically valid because it only contains alphanumeric characters, but it is not valid if the input is only expected to contain colors such as "red" or "blue."
- Do not rely exclusively on looking for malicious or malformed inputs. This is likely to miss at least one undesirable input, especially if the code's environment changes. This can give attackers enough room to bypass the intended validation. However, denylists can be useful for detecting potential attacks or determining which inputs are so malformed that they should be rejected outright.
- When validating filenames, use stringent allowlists that limit the character set to be used. If feasible, only allow a single "." character in the filename to avoid weaknesses such as CWE-23, and exclude directory separators such as "/" to avoid CWE-36. Use a list of allowable file extensions, which will help to avoid CWE-434.
- Do not rely exclusively on a filtering mechanism that removes potentially dangerous characters. This is equivalent to a denylist, which may be incomplete (CWE-184). For example, filtering "/" is insufficient protection if the filesystem also supports the use of "\" as a directory separator. Another possible error could occur when the filtering is applied in a way that still produces dangerous data (CWE-182). For example, if "../" sequences are removed from the ".../...//" string in a sequential fashion, two instances of "../" would be removed from the original string, but the remaining characters would still form the "../" string.
Mitigation MIT-15
For any security checks that are performed on the client side, ensure that these checks are duplicated on the server side, in order to avoid CWE-602. Attackers can bypass the client-side checks by modifying values after the checks have been performed, or by changing the client to remove the client-side checks entirely. Then, these modified values would be submitted to the server.
Mitigation MIT-20.1
Strategy: Input Validation
- Inputs should be decoded and canonicalized to the application's current internal representation before being validated (CWE-180). Make sure that the application does not decode the same input twice (CWE-174). Such errors could be used to bypass allowlist validation schemes by introducing dangerous inputs after they have been checked.
- Use a built-in path canonicalization function (such as realpath() in C) that produces the canonical version of the pathname, which effectively removes ".." sequences and symbolic links (CWE-23, CWE-59). This includes:
- realpath() in C
- getCanonicalPath() in Java
- GetFullPath() in ASP.NET
- realpath() or abs_path() in Perl
- realpath() in PHP
Mitigation MIT-4
Strategy: Libraries or Frameworks
Use a vetted library or framework that does not allow this weakness to occur or provides constructs that make this weakness easier to avoid [REF-1482].
Mitigation MIT-29
Strategy: Firewall
Use an application firewall that can detect attacks against this weakness. It can be beneficial in cases in which the code cannot be fixed (because it is controlled by a third party), as an emergency prevention measure while more comprehensive software assurance measures are applied, or to provide defense in depth [REF-1481].
Mitigation MIT-17
Strategy: Environment Hardening
Run your code using the lowest privileges that are required to accomplish the necessary tasks [REF-76]. If possible, create isolated accounts with limited privileges that are only used for a single task. That way, a successful attack will not immediately give the attacker access to the rest of the software or its environment. For example, database applications rarely need to run as the database administrator, especially in day-to-day operations.
Mitigation MIT-21.1
Strategy: Enforcement by Conversion
- When the set of acceptable objects, such as filenames or URLs, is limited or known, create a mapping from a set of fixed input values (such as numeric IDs) to the actual filenames or URLs, and reject all other inputs.
- For example, ID 1 could map to "inbox.txt" and ID 2 could map to "profile.txt". Features such as the ESAPI AccessReferenceMap [REF-185] provide this capability.
Mitigation MIT-22
Strategy: Sandbox or Jail
- Run the code in a "jail" or similar sandbox environment that enforces strict boundaries between the process and the operating system. This may effectively restrict which files can be accessed in a particular directory or which commands can be executed by the software.
- OS-level examples include the Unix chroot jail, AppArmor, and SELinux. In general, managed code may provide some protection. For example, java.io.FilePermission in the Java SecurityManager allows the software to specify restrictions on file operations.
- This may not be a feasible solution, and it only limits the impact to the operating system; the rest of the application may still be subject to compromise.
- Be careful to avoid CWE-243 and other weaknesses related to jails.
Mitigation MIT-34
Strategy: Attack Surface Reduction
- Store library, include, and utility files outside of the web document root, if possible. Otherwise, store them in a separate directory and use the web server's access control capabilities to prevent attackers from directly requesting them. One common practice is to define a fixed constant in each calling program, then check for the existence of the constant in the library/include file; if the constant does not exist, then the file was directly requested, and it can exit immediately.
- This significantly reduces the chance of an attacker being able to bypass any protection mechanisms that are in the base program but not in the include files. It will also reduce the attack surface.
Mitigation MIT-39
- Ensure that error messages only contain minimal details that are useful to the intended audience and no one else. The messages need to strike the balance between being too cryptic (which can confuse users) or being too detailed (which may reveal more than intended). The messages should not reveal the methods that were used to determine the error. Attackers can use detailed information to refine or optimize their original attack, thereby increasing their chances of success.
- If errors must be captured in some detail, record them in log messages, but consider what could occur if the log messages can be viewed by attackers. Highly sensitive information such as passwords should never be saved to log files.
- Avoid inconsistent messaging that might accidentally tip off an attacker about internal state, such as whether a user account exists or not.
- In the context of path traversal, error messages which disclose path information can help attackers craft the appropriate attack strings to move through the file system hierarchy.
Mitigation MIT-16
Strategy: Environment Hardening
When using PHP, configure the application so that it does not use register_globals. During implementation, develop the application so that it does not rely on this feature, but be wary of implementing a register_globals emulation that is subject to weaknesses such as CWE-95, CWE-621, and similar issues.
CAPEC-126: Path Traversal
An adversary uses path manipulation methods to exploit insufficient input validation of a target to obtain access to data that should be not be retrievable by ordinary well-formed requests. A typical variety of this attack involves specifying a path to a desired file together with dot-dot-slash characters, resulting in the file access API or function traversing out of the intended directory structure and into the root file system. By replacing or modifying the expected path information the access function or API retrieves the file desired by the attacker. These attacks either involve the attacker providing a complete path to a targeted file or using control characters (e.g. path separators (/ or \) and/or dots (.)) to reach desired directories or files.
CAPEC-64: Using Slashes and URL Encoding Combined to Bypass Validation Logic
This attack targets the encoding of the URL combined with the encoding of the slash characters. An attacker can take advantage of the multiple ways of encoding a URL and abuse the interpretation of the URL. A URL may contain special character that need special syntax handling in order to be interpreted. Special characters are represented using a percentage character followed by two digits representing the octet code of the original character (%HEX-CODE). For instance US-ASCII space character would be represented with %20. This is often referred as escaped ending or percent-encoding. Since the server decodes the URL from the requests, it may restrict the access to some URL paths by validating and filtering out the URL requests it received. An attacker will try to craft an URL with a sequence of special characters which once interpreted by the server will be equivalent to a forbidden URL. It can be difficult to protect against this attack since the URL can contain other format of encoding such as UTF-8 encoding, Unicode-encoding, etc.
CAPEC-76: Manipulating Web Input to File System Calls
An attacker manipulates inputs to the target software which the target software passes to file system calls in the OS. The goal is to gain access to, and perhaps modify, areas of the file system that the target software did not intend to be accessible.
CAPEC-78: Using Escaped Slashes in Alternate Encoding
This attack targets the use of the backslash in alternate encoding. An adversary can provide a backslash as a leading character and causes a parser to believe that the next character is special. This is called an escape. By using that trick, the adversary tries to exploit alternate ways to encode the same character which leads to filter problems and opens avenues to attack.
CAPEC-79: Using Slashes in Alternate Encoding
This attack targets the encoding of the Slash characters. An adversary would try to exploit common filtering problems related to the use of the slashes characters to gain access to resources on the target host. Directory-driven systems, such as file systems and databases, typically use the slash character to indicate traversal between directories or other container components. For murky historical reasons, PCs (and, as a result, Microsoft OSs) choose to use a backslash, whereas the UNIX world typically makes use of the forward slash. The schizophrenic result is that many MS-based systems are required to understand both forms of the slash. This gives the adversary many opportunities to discover and abuse a number of common filtering problems. The goal of this pattern is to discover server software that only applies filters to one version, but not the other.