<?xml version='1.0' encoding='UTF-8'?>
<?xml-stylesheet href="/static/style.xsl" type="text/xsl"?>
<feed xmlns="http://www.w3.org/2005/Atom" xml:lang="en">
  <id>https://cve.radiocsirt.org/rss/recent/all/10</id>
  <title>Most recent entries from all</title>
  <updated>2026-10-19T02:33:39.232006+00:00</updated>
  <author>
    <name>Vulnerability-Lookup</name>
    <email>csirt@opendfir.org</email>
  </author>
  <link href="https://cve.radiocsirt.org" rel="alternate"/>
  <generator uri="https://lkiesow.github.io/python-feedgen" version="1.0.0">python-feedgen</generator>
  <subtitle>Contains only the most 10 recent entries.</subtitle>
  <entry>
    <id>https://cve.radiocsirt.org/vuln/bdu:2024-02342</id>
    <title>bdu:2024-02342</title>
    <updated>2026-10-19T02:33:39.299748+00:00</updated>
    <content>bdu:2024-02342</content>
    <link href="https://cve.radiocsirt.org/vuln/bdu:2024-02342"/>
  </entry>
  <entry>
    <id>https://cve.radiocsirt.org/vuln/euvd-2026-158339</id>
    <title>EUVD-2026-158339</title>
    <updated>2026-10-19T02:33:39.299802+00:00</updated>
    <content>EUVD-2026-158339</content>
    <link href="https://cve.radiocsirt.org/vuln/euvd-2026-158339"/>
  </entry>
  <entry>
    <id>https://cve.radiocsirt.org/vuln/fkie_cve-2024-28105</id>
    <title>fkie_cve-2024-28105</title>
    <updated>2026-10-19T02:33:39.299823+00:00</updated>
    <content type="xhtml">
      <div xmlns="http://www.w3.org/1999/xhtml">
        <p>phpMyFAQ is an open source FAQ web application for PHP 8.1+ and MySQL, PostgreSQL and other databases. The category image upload function in phpmyfaq is vulnerable to manipulation of the `Content-type` and `lang` parameters, allowing attackers to upload malicious files with a .php extension, potentially leading to remote code execution (RCE) on the system. This vulnerability is fixed in 3.2.6.</p>
      </div>
    </content>
    <link href="https://cve.radiocsirt.org/vuln/fkie_cve-2024-28105"/>
  </entry>
  <entry>
    <id>https://cve.radiocsirt.org/vuln/ghsa-pwh2-fpfr-x5gf</id>
    <title>GHSA-pwh2-fpfr-x5gf — phpMyFAQ's File Upload Bypass at Category Image Leads to RCE</title>
    <updated>2026-10-19T02:33:39.299865+00:00</updated>
    <content type="xhtml">
      <div xmlns="http://www.w3.org/1999/xhtml"><p><strong>Affected:</strong> Packagist: phpmyfaq/phpmyfaq</p>
<p>### Summary
The category image upload function in phpmyfaq is vulnerable to manipulation of the `Content-type` and `lang` parameters, allowing attackers to upload malicious files with a .php extension, potentially leading to remote code execution (RCE) on the system.</p>
<p>### Details
In the file upload function of the category image, the `Content-type` can be manipulated to return an empty string for the extension and the `lang` parameter can be set to `.php.` to allow an attacker to save a file as `.PHP`. This allows the uploading of web shells which could lead to RCE on phpmyfaq.</p>
<p>### PoC
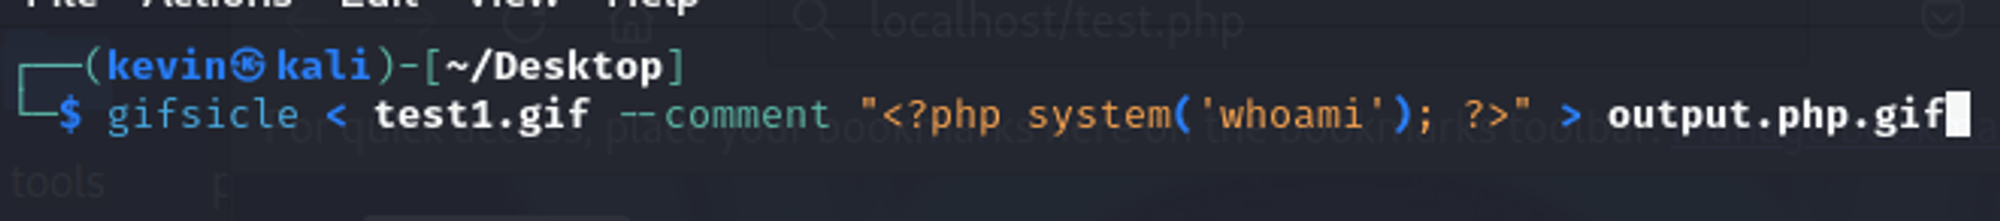
1. Generate a fake .GIF file that contains a php command using the tool `gifsicle`
    a. Cmd: `gifsicle &lt; test1.gif --comment "&lt;?php system('whoami'); ?&gt;" &gt; output.php.gif`
  
    ![image](https://github.com/thorsten/phpMyFAQ/assets/63487456/b9fc1f37-ce83-4ec5-88a5-5217c35caac9)</p>
<p>b. The contents of the file should look like this:  

     ![image](https://github.com/thorsten/phpMyFAQ/assets/63487456/6d64a5b9-238f-4b56-8de6-7a765f69b0f5)</p>
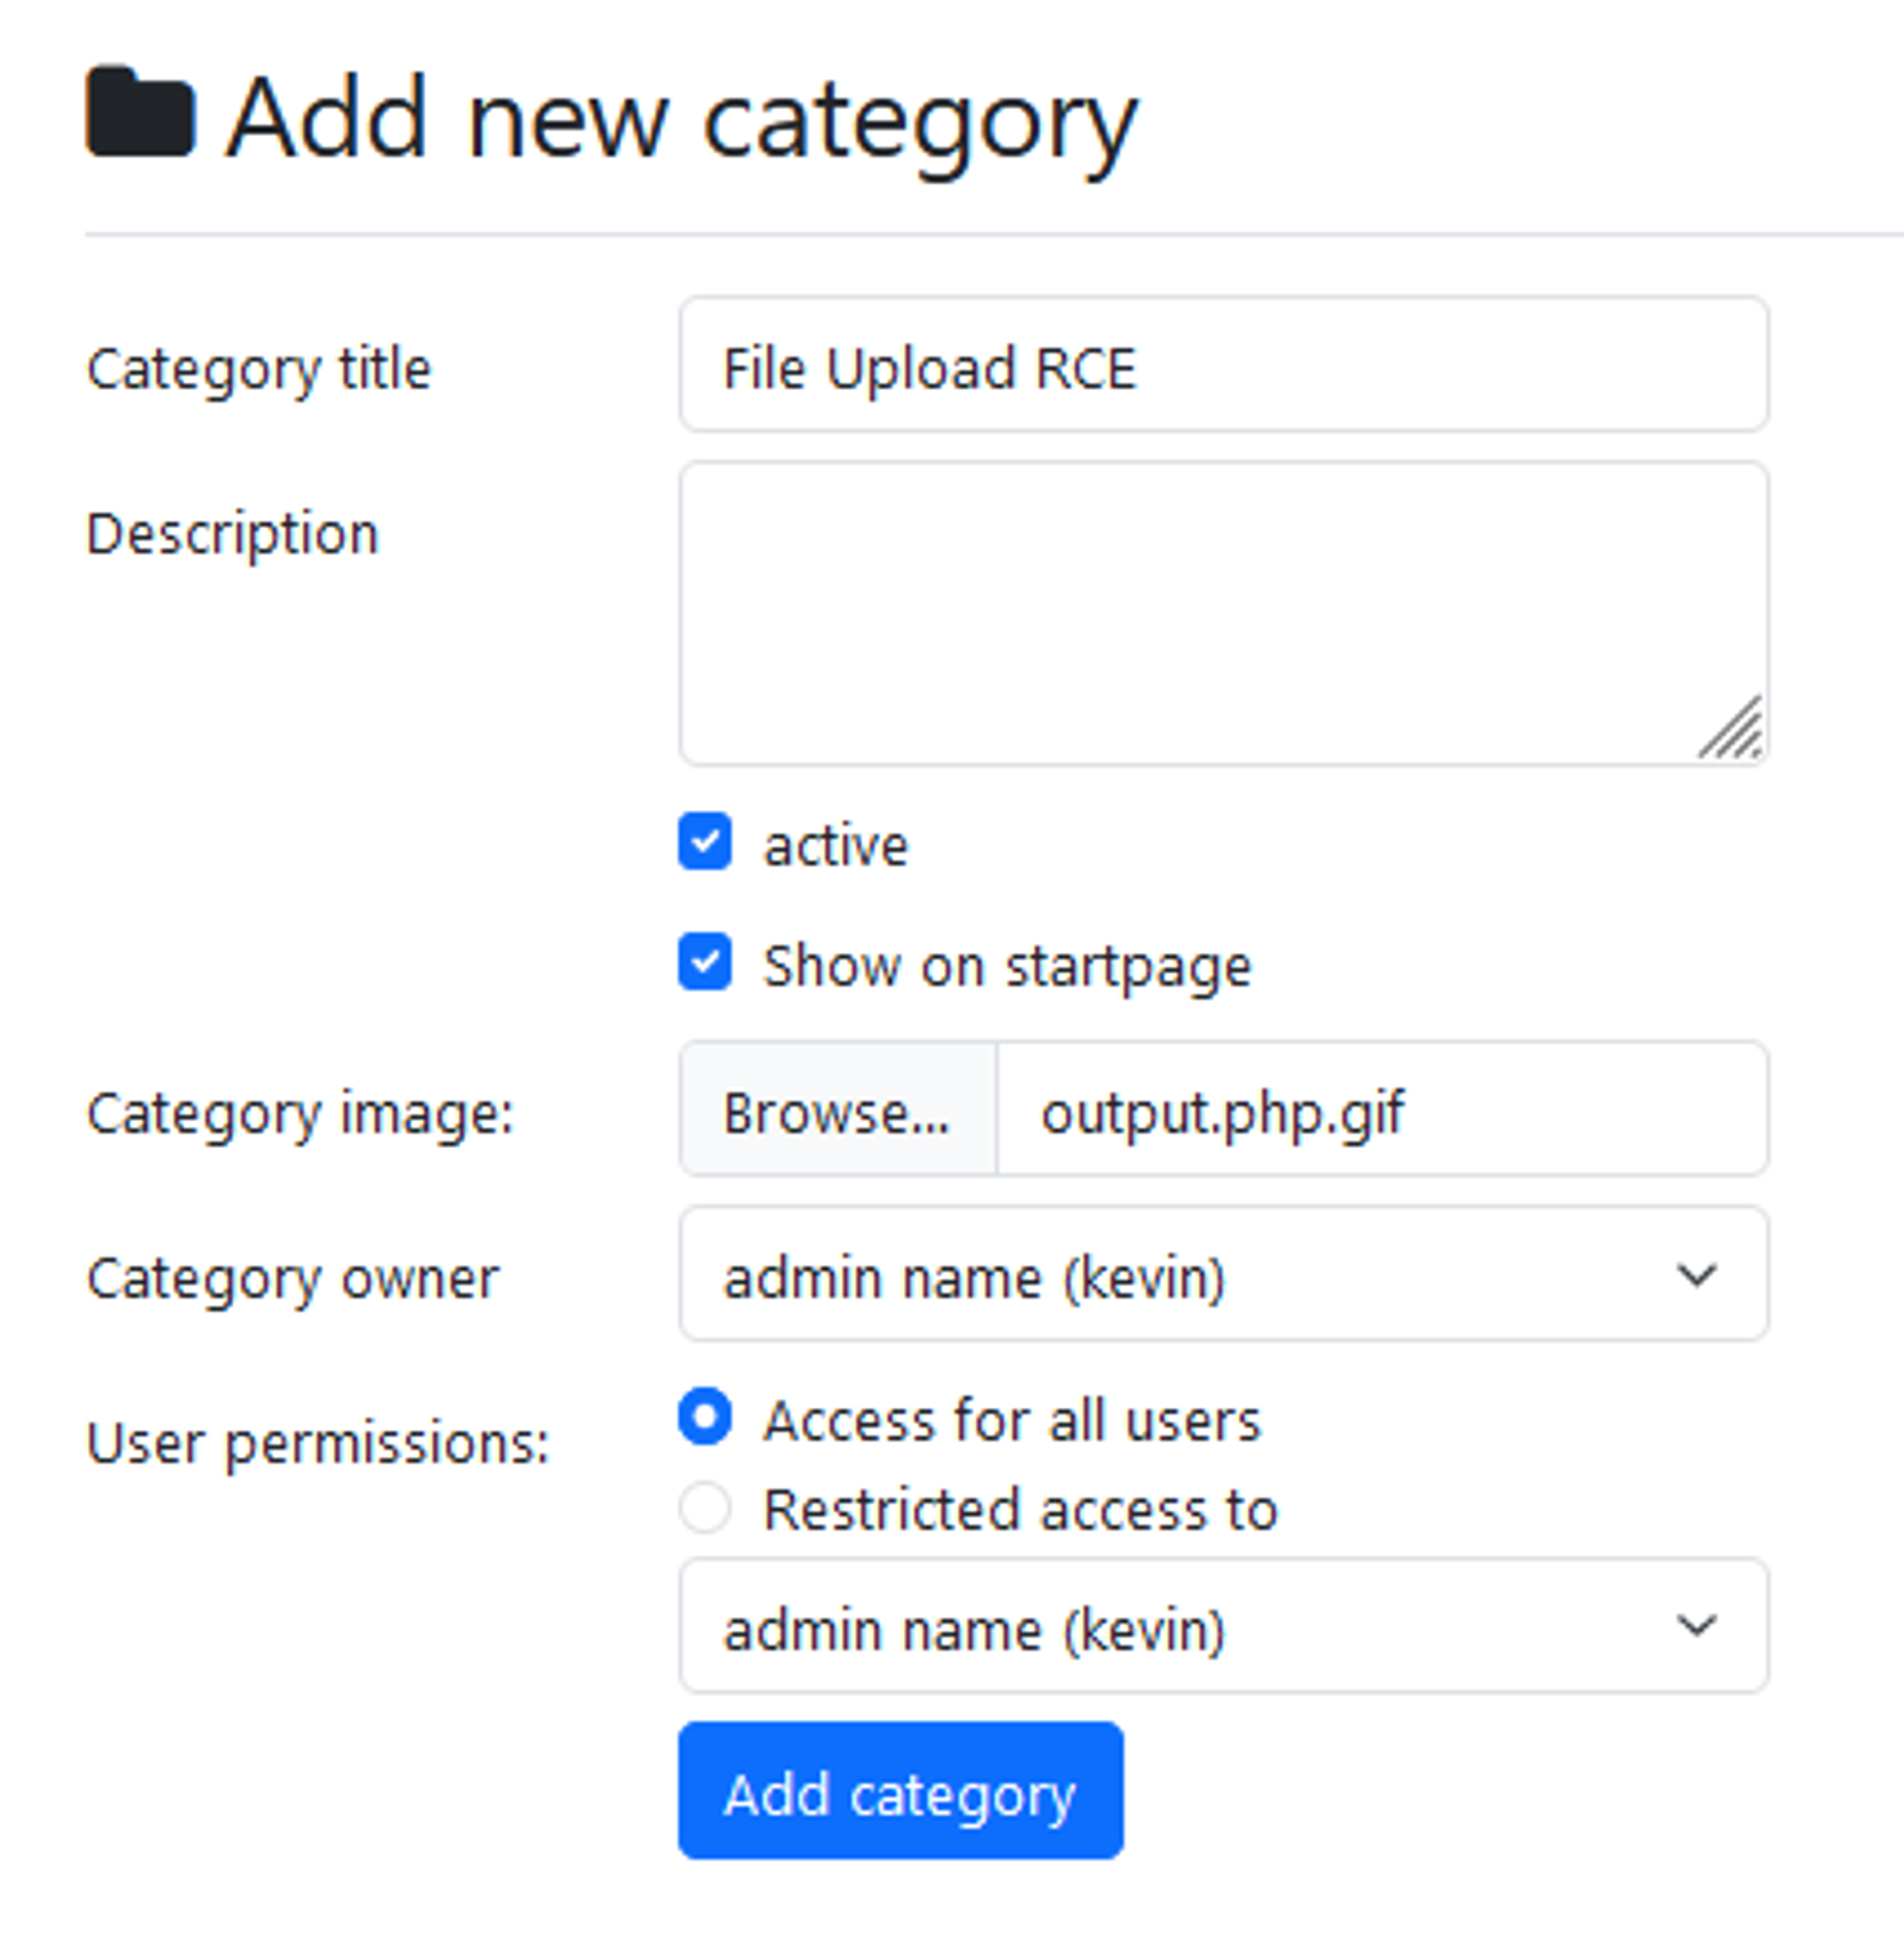
<p>2.  Browse to “../phpmyfaq/admin/?action=addcategory” and upload the fake .GIF file
    ![image](https://github.com/thorsten/phpMyFAQ/assets/63487456/680f1c94-c4eb-4873-be05-018e745b88b2)</p>
<p>3.  Intercept the upload request and modify the params below and forward it:
    3a. `lang` parameter to `.php.`
    3b. `Content-Type` parameter from `image/gif` to `image/gif2`</p>
<p>![image](https://github.com/thorsten/phpMyFAQ/assets/63487456/9247c5bb-8f58-41de-a5d4-8…</p></div>
    </content>
    <link href="https://cve.radiocsirt.org/vuln/ghsa-pwh2-fpfr-x5gf"/>
  </entry>
  <entry>
    <id>https://cve.radiocsirt.org/vuln/gsd-2024-28105</id>
    <title>gsd-2024-28105</title>
    <updated>2026-10-19T02:33:39.299966+00:00</updated>
    <content>gsd-2024-28105</content>
    <link href="https://cve.radiocsirt.org/vuln/gsd-2024-28105"/>
  </entry>
</feed>