<?xml version='1.0' encoding='UTF-8'?>
<?xml-stylesheet href="/static/style.xsl" type="text/xsl"?>
<feed xmlns="http://www.w3.org/2005/Atom" xml:lang="en">
  <id>https://cve.radiocsirt.org/rss/recent/all/10</id>
  <title>Most recent entries from all</title>
  <updated>2026-10-10T15:31:06.407015+00:00</updated>
  <author>
    <name>Vulnerability-Lookup</name>
    <email>csirt@opendfir.org</email>
  </author>
  <link href="https://cve.radiocsirt.org" rel="alternate"/>
  <generator uri="https://lkiesow.github.io/python-feedgen" version="1.0.0">python-feedgen</generator>
  <subtitle>Contains only the most 10 recent entries.</subtitle>
  <entry>
    <id>https://cve.radiocsirt.org/vuln/euvd-2026-10192</id>
    <title>EUVD-2026-10192</title>
    <updated>2026-10-10T15:31:06.410093+00:00</updated>
    <content>EUVD-2026-10192</content>
    <link href="https://cve.radiocsirt.org/vuln/euvd-2026-10192"/>
  </entry>
  <entry>
    <id>https://cve.radiocsirt.org/vuln/fkie_cve-2023-49276</id>
    <title>fkie_cve-2023-49276</title>
    <updated>2026-10-10T15:31:06.410143+00:00</updated>
    <content type="xhtml">
      <div xmlns="http://www.w3.org/1999/xhtml">
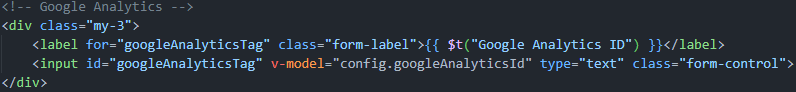
        <p>Uptime Kuma is an open source self-hosted monitoring tool. In affected versions the Google Analytics element in vulnerable to Attribute Injection leading to Cross-Site-Scripting (XSS). Since the custom status interface can set an independent Google Analytics ID and the template has not been sanitized, there is an attribute injection vulnerability here, which can lead to XSS attacks. This vulnerability has been addressed in commit `f28dccf4e` which is included in release version 1.23.7. Users are advised to upgrade. There are no known workarounds for this vulnerability.</p>
      </div>
    </content>
    <link href="https://cve.radiocsirt.org/vuln/fkie_cve-2023-49276"/>
  </entry>
  <entry>
    <id>https://cve.radiocsirt.org/vuln/ghsa-v4v2-8h88-65qj</id>
    <title>GHSA-v4v2-8h88-65qj — Attribute Injection leading to XSS(Cross-Site-Scripting)</title>
    <updated>2026-10-10T15:31:06.410188+00:00</updated>
    <content type="xhtml">
      <div xmlns="http://www.w3.org/1999/xhtml"><p><strong>Affected:</strong> npm: uptime-kuma</p>
<p>### Summary
Google Analytics element Attribute Injection leading to XSS</p>
<p>### Details
Since the custom status interface can set an independent Google Analytics ID and the template has not been sanitized, there is an attribute injection vulnerability here, which can lead to XSS attacks.
![image](https://user-images.githubusercontent.com/110759348/282278047-667b774b-421f-449a-8f95-3f3906ae4216.png)</p>
<p>### PoC
1. Run the latest version of the louislam/uptime-kuma container and initialize the account password.
2. Create a new status page.
3. Edit the status page and change the Google Analytics ID to following payload(it only works for firefox. Any attribute can be injected, but this seems the most intuitive):
```
123123" onafterscriptexecute=alert(window.name+1),eval(window.name) a="x
```</p>
<p>4. Click Save and return to the interface. XSS occurs.
screenshots:
![image](https://user-images.githubusercontent.com/110759348/282287393-4874974f-9416-4941-9c2e-a92ee2412197.png)</p>
<p>![9d0603e634fb7da2e83a0a45dc0a36ac](https://user-images.githubusercontent.com/110759348/282287346-1deb0382-520f-47cf-b191-9b7d19c47879.png)</p></div>
    </content>
    <link href="https://cve.radiocsirt.org/vuln/ghsa-v4v2-8h88-65qj"/>
  </entry>
  <entry>
    <id>https://cve.radiocsirt.org/vuln/gsd-2023-49276</id>
    <title>gsd-2023-49276</title>
    <updated>2026-10-10T15:31:06.410252+00:00</updated>
    <content>gsd-2023-49276</content>
    <link href="https://cve.radiocsirt.org/vuln/gsd-2023-49276"/>
  </entry>
</feed>
