<?xml version='1.0' encoding='UTF-8'?>
<?xml-stylesheet href="/static/style.xsl" type="text/xsl"?>
<feed xmlns="http://www.w3.org/2005/Atom" xml:lang="en">
  <id>https://cve.radiocsirt.org/rss/recent/all/10</id>
  <title>Most recent entries from all</title>
  <updated>2026-10-03T13:42:14.613411+00:00</updated>
  <author>
    <name>Vulnerability-Lookup</name>
    <email>csirt@opendfir.org</email>
  </author>
  <link href="https://cve.radiocsirt.org" rel="alternate"/>
  <generator uri="https://lkiesow.github.io/python-feedgen" version="1.0.0">python-feedgen</generator>
  <subtitle>Contains only the most 10 recent entries.</subtitle>
  <entry>
    <id>https://cve.radiocsirt.org/vuln/euvd-2026-330400</id>
    <title>EUVD-2026-330400</title>
    <updated>2026-10-03T13:42:14.622169+00:00</updated>
    <content>EUVD-2026-330400</content>
    <link href="https://cve.radiocsirt.org/vuln/euvd-2026-330400"/>
  </entry>
  <entry>
    <id>https://cve.radiocsirt.org/vuln/fkie_cve-2026-52796</id>
    <title>fkie_cve-2026-52796</title>
    <updated>2026-10-03T13:42:14.622211+00:00</updated>
    <content type="xhtml">
      <div xmlns="http://www.w3.org/1999/xhtml">
        <p>Gogs is an open source self-hosted Git service. Prior to 0.14.3, specially crafted issue index pattern can cause a panic when rendering, resulting in denial of service. In internal/markup/markup.go, RenderIssueIndexPattern renders the issue index pattern to a link using com.Expand, which is not safe: when the configured pattern contains an opening brace { but no closing brace }, strings.Index(template, "}") returns -1 and the subsequent slice template[:-1] triggers a panic. Once such a pattern is set, any page in the affected repository that contains an issue index reference such as #1 becomes unavailable. This vulnerability is fixed in 0.14.3.</p>
      </div>
    </content>
    <link href="https://cve.radiocsirt.org/vuln/fkie_cve-2026-52796"/>
  </entry>
  <entry>
    <id>https://cve.radiocsirt.org/vuln/ghsa-4j89-2c4f-44c6</id>
    <title>GHSA-4j89-2c4f-44c6 — Gogs has DoS in rendering issue index pattern</title>
    <updated>2026-10-03T13:42:14.622251+00:00</updated>
    <content type="xhtml">
      <div xmlns="http://www.w3.org/1999/xhtml"><p><strong>Affected:</strong> Go: gogs.io/gogs</p>
<p>### Summary
Special template of issue index pattern may cause panic.</p>
<p>### Details</p>
<p>in internal/markup/markup.go</p>
<p>```go
link = fmt.Sprintf(`&lt;a href="%s"&gt;%s&lt;/a&gt;`, com.Expand(metas["format"], metas), m)
```</p>
<p>Issue index pattern is rendered to link with `com.Expand`.</p>
<p>However, `com.Expand` is not safe.</p>
<p>```go
i = strings.Index(template, "}")
if s, ok := match[template[:i]]; ok {
```</p>
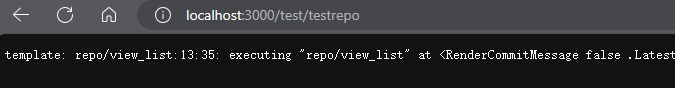
<p>when `{` is found but `}` not found, i comes to 1, template[:-1] will be called, and then panicked</p>
<p>![image](https://user-images.githubusercontent.com/38121125/285883766-64873c44-d325-44ce-96a8-badbaadab178.png)</p>
<p>finally, all pages than contains issue index are unavailable.</p>
<p>### PoC</p>
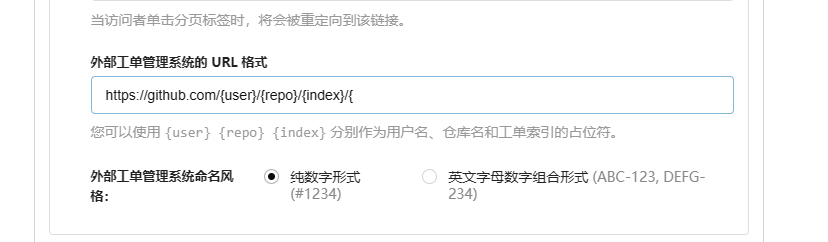
<p>1. set issue index pattern as follow</p>
<p>![image](https://user-images.githubusercontent.com/38121125/285878157-c5fe848e-0fbd-4fdb-92d4-5eb01df2b8ca.png)</p>
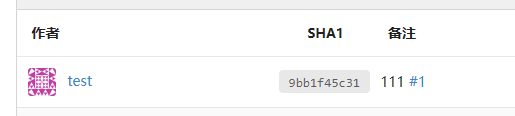
<p>2. add a commit which point to an issue in its msg</p>
<p>![image](https://user-images.githubusercontent.com/38121125/285879545-bc360503-49b9-453f-aa24-9a5c5a45cf10.png)</p>
<p>using `#1` above</p>
<p>### Impact</p>
<p>DoS that cause part of pages of the specify repo unavailable.</p></div>
    </content>
    <link href="https://cve.radiocsirt.org/vuln/ghsa-4j89-2c4f-44c6"/>
  </entry>
  <entry>
    <id>https://cve.radiocsirt.org/vuln/wid-sec-w-2026-2013</id>
    <title>WID-SEC-W-2026-2013 — Gogs: Mehrere Schwachstellen</title>
    <updated>2026-10-03T13:42:14.622298+00:00</updated>
    <content type="xhtml">
      <div xmlns="http://www.w3.org/1999/xhtml">
        <p>Ein Angreifer kann mehrere Schwachstellen in Gogs ausnutzen, um erweiterte Berechtigungen zu erlangen, beliebigen Code auszuführen – sogar mit erweiterten Berechtigungen, was zur vollständigen Kontrolle über das System führen kann –, Sicherheitsmaßnahmen zu umgehen, Daten zu manipulieren, Cross-Site-Scripting-Angriffe durchzuführen, Benutzer auf bösartige Websites umzuleiten oder einen Denial-of-Service-Zustand zu verursachen.</p>
      </div>
    </content>
    <link href="https://cve.radiocsirt.org/vuln/wid-sec-w-2026-2013"/>
  </entry>
</feed>