<?xml version='1.0' encoding='UTF-8'?>
<?xml-stylesheet href="/static/style.xsl" type="text/xsl"?>
<feed xmlns="http://www.w3.org/2005/Atom" xml:lang="en">
  <id>https://cve.radiocsirt.org/rss/recent/all/10</id>
  <title>Most recent entries from all</title>
  <updated>2026-10-03T05:50:19.256114+00:00</updated>
  <author>
    <name>Vulnerability-Lookup</name>
    <email>csirt@opendfir.org</email>
  </author>
  <link href="https://cve.radiocsirt.org" rel="alternate"/>
  <generator uri="https://lkiesow.github.io/python-feedgen" version="1.0.0">python-feedgen</generator>
  <subtitle>Contains only the most 10 recent entries.</subtitle>
  <entry>
    <id>https://cve.radiocsirt.org/vuln/euvd-2026-160098</id>
    <title>EUVD-2026-160098</title>
    <updated>2026-10-03T05:50:19.322012+00:00</updated>
    <content>EUVD-2026-160098</content>
    <link href="https://cve.radiocsirt.org/vuln/euvd-2026-160098"/>
  </entry>
  <entry>
    <id>https://cve.radiocsirt.org/vuln/fkie_cve-2024-27288</id>
    <title>fkie_cve-2024-27288</title>
    <updated>2026-10-03T05:50:19.322053+00:00</updated>
    <content type="xhtml">
      <div xmlns="http://www.w3.org/1999/xhtml">
        <p>1Panel is an open source Linux server operation and maintenance management panel. Prior to version 1.10.1-lts, users can use Burp to obtain unauthorized access to the console page. The vulnerability has been fixed in v1.10.1-lts. There are no known workarounds.</p>
      </div>
    </content>
    <link href="https://cve.radiocsirt.org/vuln/fkie_cve-2024-27288"/>
  </entry>
  <entry>
    <id>https://cve.radiocsirt.org/vuln/ghsa-26w3-q4j8-4xjp</id>
    <title>GHSA-26w3-q4j8-4xjp — 1Panel open source panel project has an unauthorized vulnerability.</title>
    <updated>2026-10-03T05:50:19.322088+00:00</updated>
    <content type="xhtml">
      <div xmlns="http://www.w3.org/1999/xhtml"><p><strong>Affected:</strong> Go: github.com/1Panel-dev/1Panel</p>
<p>### Impact</p>
<p>The steps are as follows:</p>
<p>1. Access https://IP:PORT/ in the browser, which prompts the user to access with a secure entry point.
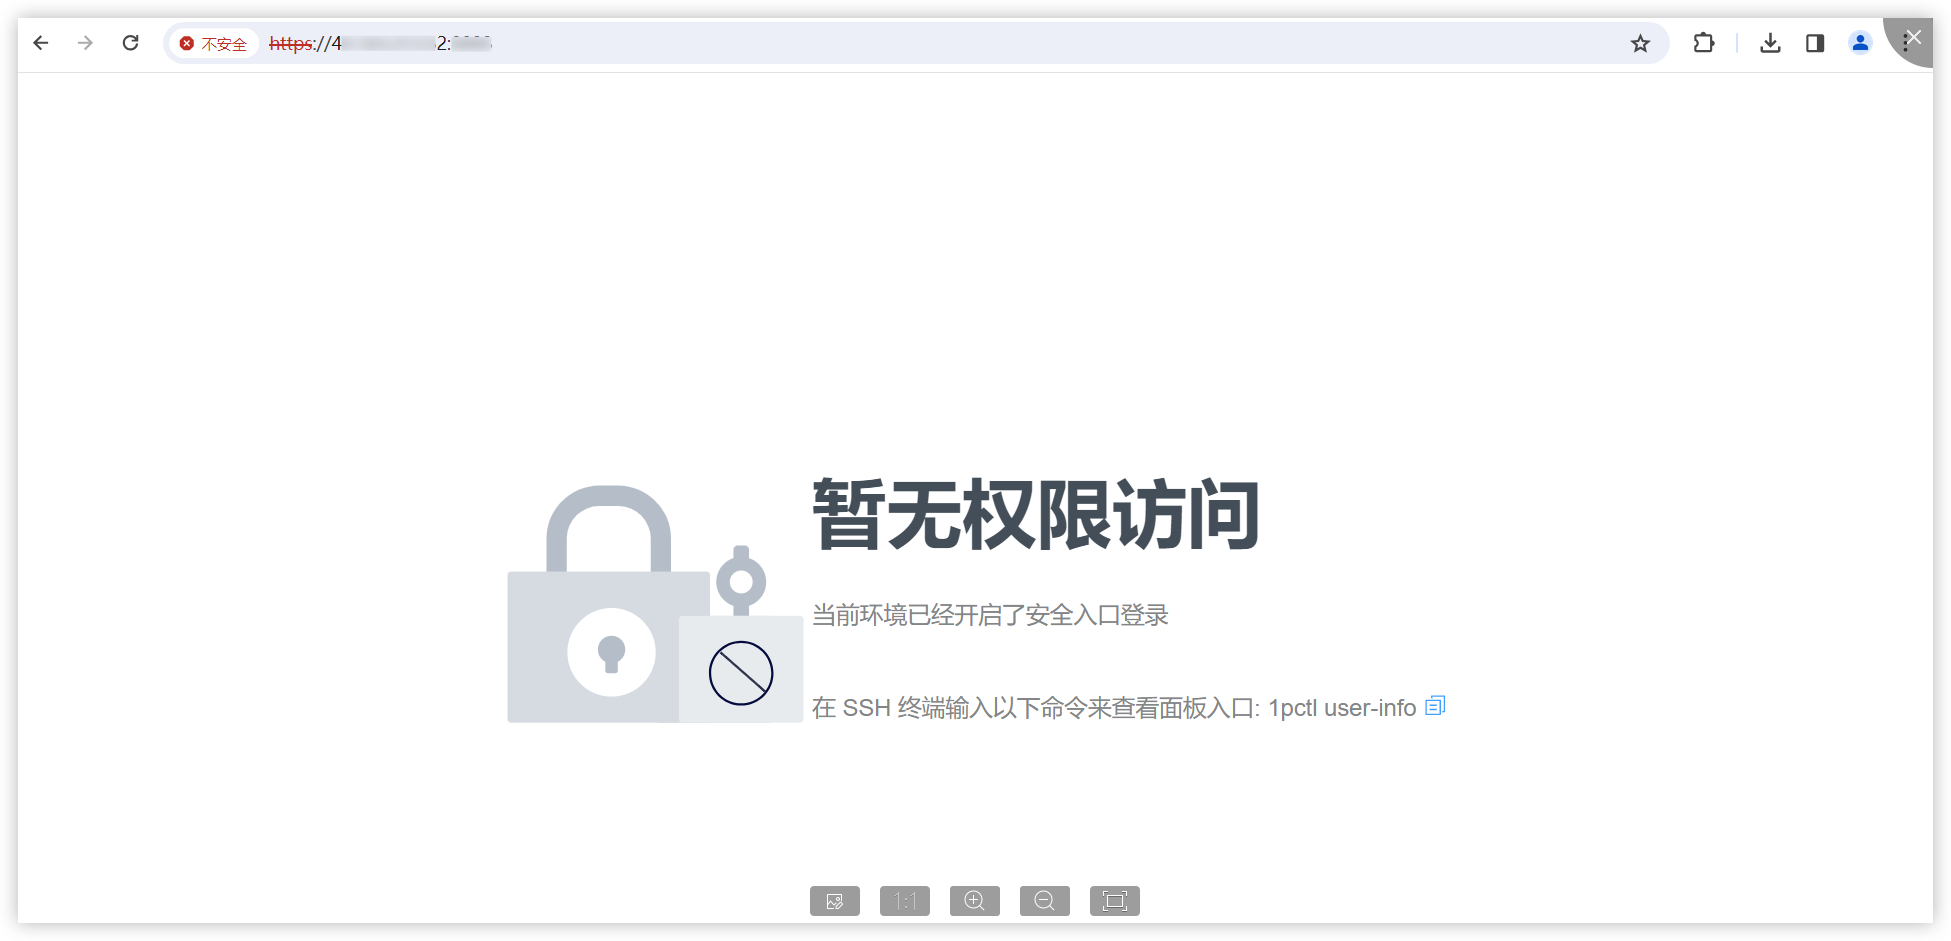
![image](https://github.com/1Panel-dev/1Panel/assets/46734380/8dc7d81c-6cc3-4b5d-a1d4-d3c5ed2de005)</p>
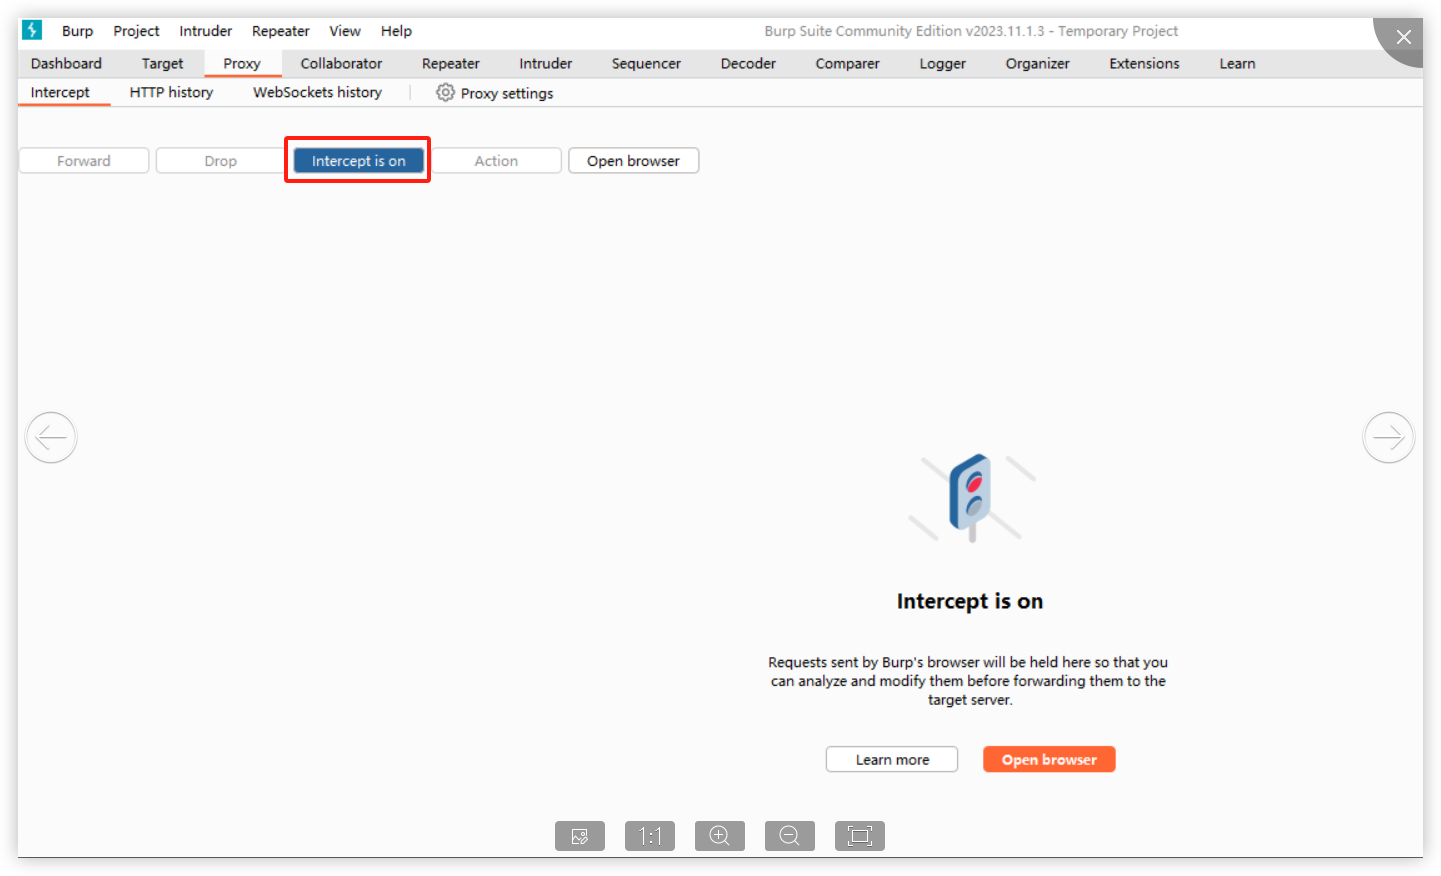
<p>2. Use Burp to intercept:
![image](https://github.com/1Panel-dev/1Panel/assets/46734380/f8e93d08-1b66-4434-8923-2e8e3dedebe3)</p>
<p>When opening the browser and entering the URL (allowing the first intercepted packet through Burp), the following is displayed:
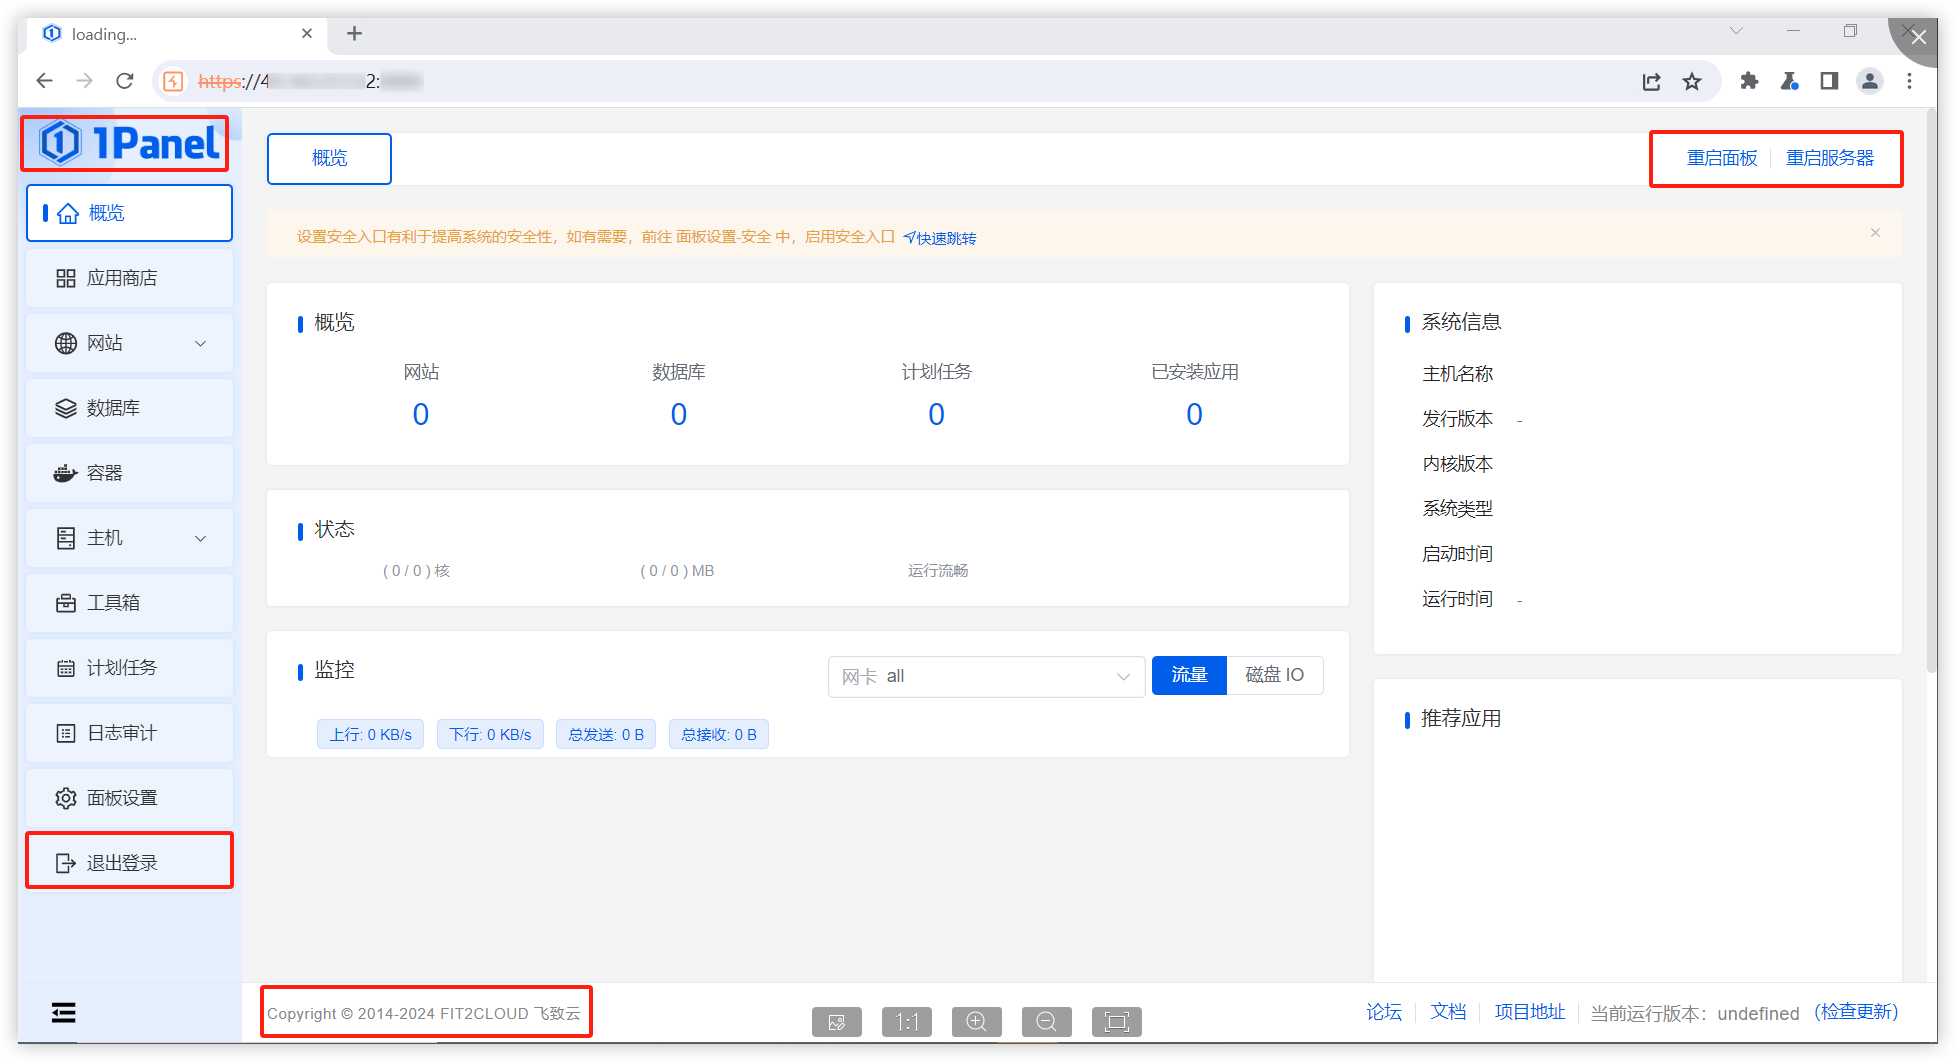
![image](https://github.com/1Panel-dev/1Panel/assets/46734380/118c0102-7c89-404d-834a-88a644482afc)</p>
<p>It is found that in this situation, we can access the console page (although no data is returned and no modification operations can be performed)."</p>
<p>Affected versions: &lt;= 1.10.0-lts</p>
<p>### Patches</p>
<p>The vulnerability has been fixed in v1.10.1-lts.</p>
<p>### Workarounds</p>
<p>It is recommended to upgrade the version to 1.10.1-lts.</p>
<p>### References</p>
<p>If you have any questions or comments about this advisory:</p>
<p>Open an issue in https://github.com/1Panel-dev/1Panel
Email us at wanghe@fit2cloud.com</p></div>
    </content>
    <link href="https://cve.radiocsirt.org/vuln/ghsa-26w3-q4j8-4xjp"/>
  </entry>
  <entry>
    <id>https://cve.radiocsirt.org/vuln/gsd-2024-27288</id>
    <title>gsd-2024-27288</title>
    <updated>2026-10-03T05:50:19.322131+00:00</updated>
    <content>gsd-2024-27288</content>
    <link href="https://cve.radiocsirt.org/vuln/gsd-2024-27288"/>
  </entry>
</feed>