CWE-862
Allowed-with-ReviewMissing Authorization
Abstraction: Class · Status: Incomplete
The product does not perform an authorization check when an actor attempts to access a resource or perform an action.
18003 vulnerabilities reference this CWE, most recent first.
GHSA-FCP5-57P2-VF46
Vulnerability from github – Published: 2022-04-13 00:00 – Updated: 2022-04-20 00:00A vulnerability has been identified in SICAM A8000 CP-8031 (All versions < V4.80), SICAM A8000 CP-8050 (All versions < V4.80). Affected devices do not require an user to be authenticated to access certain files. This could allow unauthenticated attackers to download these files.
{
  "affected": [],
  "aliases": [
    "CVE-2022-27480"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-425",
      "CWE-862"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2022-04-12T09:15:00Z",
    "severity": "HIGH"
  },
  "details": "A vulnerability has been identified in SICAM A8000 CP-8031 (All versions \u003c V4.80), SICAM A8000 CP-8050 (All versions \u003c V4.80). Affected devices do not require an user to be authenticated to access certain files. This could allow unauthenticated attackers to download these files.",
  "id": "GHSA-fcp5-57p2-vf46",
  "modified": "2022-04-20T00:00:50Z",
  "published": "2022-04-13T00:00:31Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2022-27480"
    },
    {
      "type": "WEB",
      "url": "https://cert-portal.siemens.com/productcert/pdf/ssa-316850.pdf"
    },
    {
      "type": "WEB",
      "url": "http://packetstormsecurity.com/files/166743/Siemens-A8000-CP-8050-CP-8031-SICAM-WEB-Missing-File-Download-Missing-Authentication.html"
    },
    {
      "type": "WEB",
      "url": "http://seclists.org/fulldisclosure/2022/Apr/20"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:N/A:N",
      "type": "CVSS_V3"
    }
  ]
}
GHSA-FCR2-G7H7-M264
Vulnerability from github – Published: 2026-09-03 21:31 – Updated: 2026-09-03 21:31Missing Authorization in Kibana Leading to Unauthorized Modification of Data / Missing Authorization (CWE-862) in Kibana can lead to unauthorized modification of data via Privilege Abuse (CAPEC-122). An authenticated user holding Security read-level access in a single Kibana space could trigger Entity Analytics migration operations that perform privileged writes across all Kibana spaces, regardless of that user's actual access scope.
{
  "affected": [],
  "aliases": [
    "CVE-2026-78596"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-862"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2026-09-03T19:17:28Z",
    "severity": "MODERATE"
  },
  "details": "Missing Authorization in Kibana Leading to Unauthorized Modification of Data / Missing Authorization (CWE-862) in Kibana can lead to unauthorized modification of data via Privilege Abuse (CAPEC-122). An authenticated user holding Security read-level access in a single Kibana space could trigger Entity Analytics migration operations that perform privileged writes across all Kibana spaces, regardless of that user\u0027s actual access scope.",
  "id": "GHSA-fcr2-g7h7-m264",
  "modified": "2026-09-03T21:31:14Z",
  "published": "2026-09-03T21:31:14Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2026-78596"
    },
    {
      "type": "WEB",
      "url": "https://discuss.elastic.co/t/kibana-8-19-21-9-4-6-9-5-3-security-update-esa-2026-154/390161"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:N/I:L/A:N",
      "type": "CVSS_V3"
    }
  ]
}
GHSA-FCR8-6Q7R-M4WG
Vulnerability from github – Published: 2021-05-04 17:42 – Updated: 2022-10-20 13:56Impact
A bypass of CVE-2020-26231 (fixed in 1.0.470/471 and 1.1.1) was discovered that has the same impact as CVE-2020-26231 & CVE-2020-15247:
An authenticated backend user with the cms.manage_pages, cms.manage_layouts, or cms.manage_partials permissions who would normally not be permitted to provide PHP code to be executed by the CMS due to cms.enableSafeMode being enabled is able to write specific Twig code to escape the Twig sandbox and execute arbitrary PHP.
This is not a problem for anyone that trusts their users with those permissions to normally write & manage PHP within the CMS by not having cms.enableSafeMode enabled, but would be a problem for anyone relying on cms.enableSafeMode to ensure that users with those permissions in production do not have access to write & execute arbitrary PHP.
Patches
Issue has been patched in Build 472 (v1.0.472) and v1.1.2.
Workarounds
Apply https://github.com/octobercms/october/commit/f63519ff1e8d375df30deba63156a2fc97aa9ee7 to your installation manually if unable to upgrade to Build 472 or v1.1.2.
References
Reported by ka1n4t
For more information
If you have any questions or comments about this advisory: * Email us at hello@octobercms.com
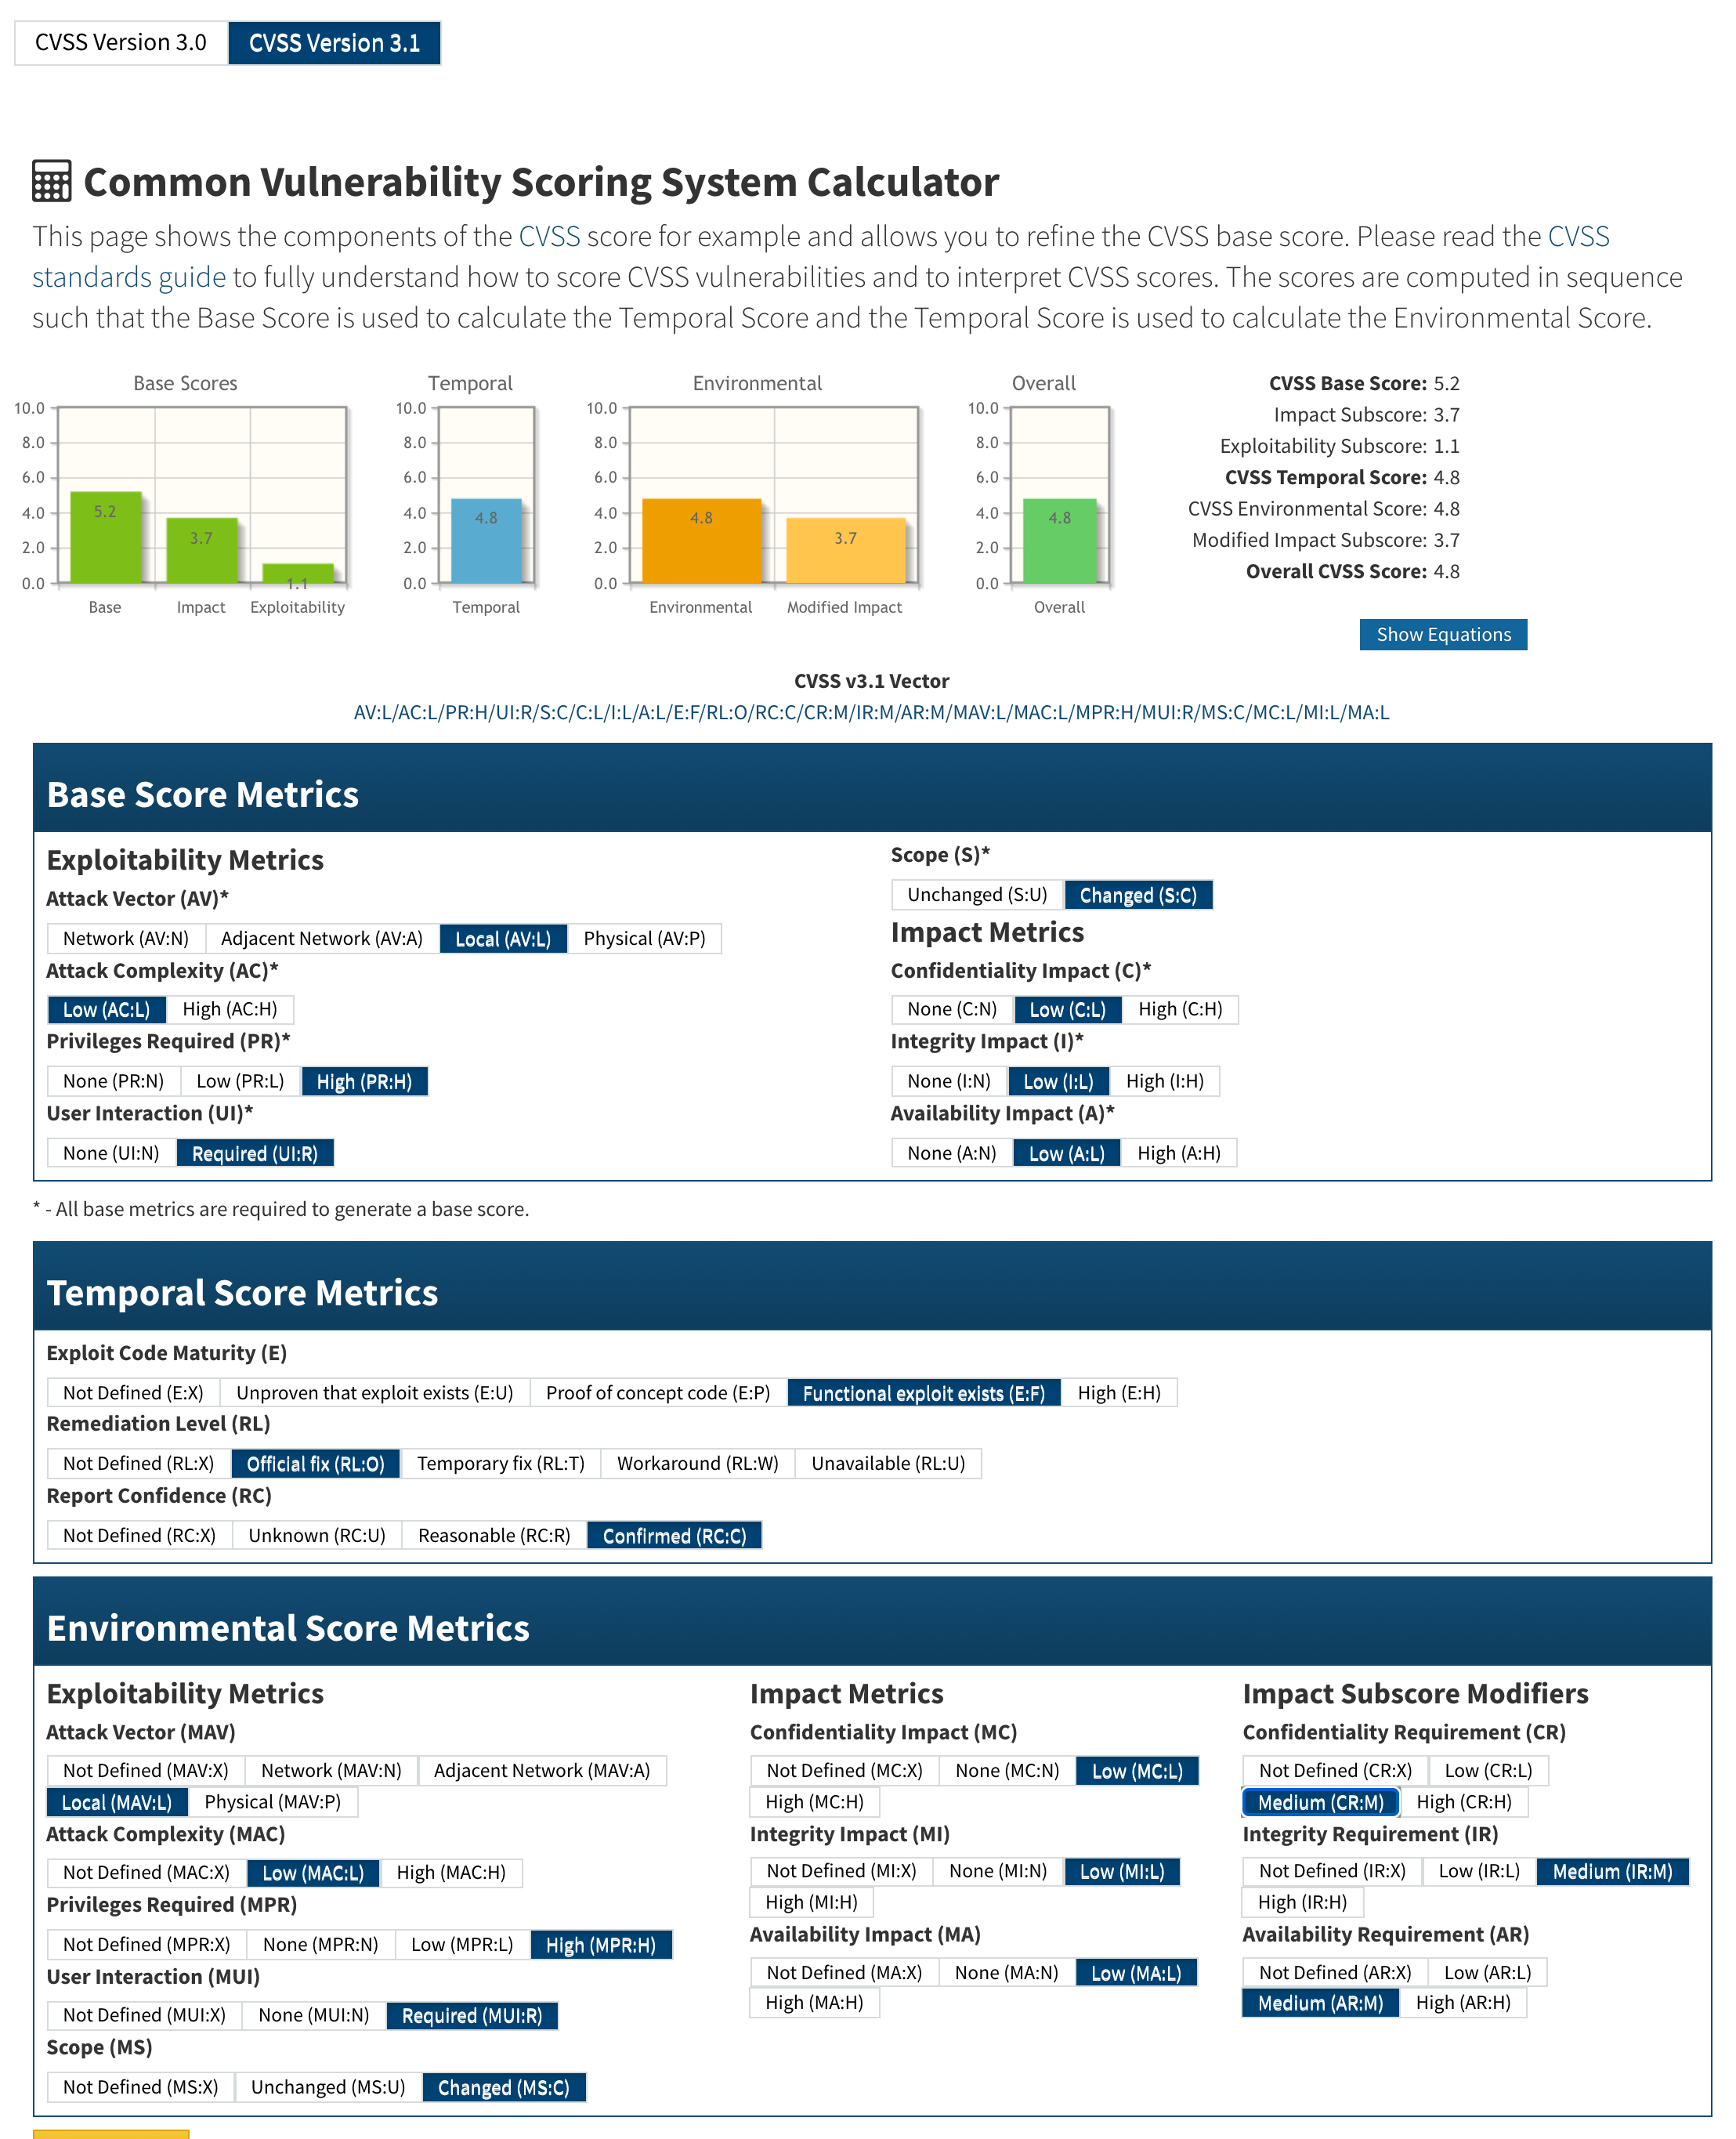
Threat assessment:
{
  "affected": [
    {
      "package": {
        "ecosystem": "Packagist",
        "name": "october/cms"
      },
      "ranges": [
        {
          "events": [
            {
              "introduced": "1.0.471"
            },
            {
              "fixed": "1.0.472"
            }
          ],
          "type": "ECOSYSTEM"
        }
      ],
      "versions": [
        "1.0.471"
      ]
    },
    {
      "package": {
        "ecosystem": "Packagist",
        "name": "october/cms"
      },
      "ranges": [
        {
          "events": [
            {
              "introduced": "1.1.1"
            },
            {
              "fixed": "1.1.2"
            }
          ],
          "type": "ECOSYSTEM"
        }
      ],
      "versions": [
        "1.1.1"
      ]
    }
  ],
  "aliases": [
    "CVE-2021-21264"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-862"
    ],
    "github_reviewed": true,
    "github_reviewed_at": "2021-05-03T15:59:55Z",
    "nvd_published_at": "2021-05-03T16:15:00Z",
    "severity": "MODERATE"
  },
  "details": "### Impact\nA bypass of CVE-2020-26231 (fixed in 1.0.470/471 and 1.1.1) was discovered that has the same impact as CVE-2020-26231 \u0026 CVE-2020-15247:\n\nAn authenticated backend user with the `cms.manage_pages`, `cms.manage_layouts`, or `cms.manage_partials` permissions who would **normally** not be permitted to provide PHP code to be executed by the CMS due to `cms.enableSafeMode` being enabled is able to write specific Twig code to escape the Twig sandbox and execute arbitrary PHP.\n\nThis is not a problem for anyone that trusts their users with those permissions to normally write \u0026 manage PHP within the CMS by not having `cms.enableSafeMode` enabled, but would be a problem for anyone relying on `cms.enableSafeMode` to ensure that users with those permissions in production do not have access to write \u0026 execute arbitrary PHP.\n\n### Patches\nIssue has been patched in Build 472 (v1.0.472) and v1.1.2.\n\n### Workarounds\nApply https://github.com/octobercms/october/commit/f63519ff1e8d375df30deba63156a2fc97aa9ee7 to your installation manually if unable to upgrade to Build 472 or v1.1.2.\n\n### References\nReported by [ka1n4t](https://github.com/ka1n4t)\n\n### For more information\nIf you have any questions or comments about this advisory:\n* Email us at [hello@octobercms.com](mailto:hello@octobercms.com)\n\n### Threat assessment:\n\u003cimg width=\"1108\" alt=\"Screen Shot 2020-10-10 at 1 21 13 PM\" src=\"https://user-images.githubusercontent.com/7253840/95663316-7de28b80-0afb-11eb-999d-a6526cf78709.png\"\u003e",
  "id": "GHSA-fcr8-6q7r-m4wg",
  "modified": "2022-10-20T13:56:32Z",
  "published": "2021-05-04T17:42:33Z",
  "references": [
    {
      "type": "WEB",
      "url": "https://github.com/octobercms/october/security/advisories/GHSA-fcr8-6q7r-m4wg"
    },
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2021-21264"
    },
    {
      "type": "PACKAGE",
      "url": "https://github.com/octobercms/october"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:L/AC:L/PR:H/UI:R/S:C/C:L/I:L/A:L",
      "type": "CVSS_V3"
    }
  ],
  "summary": "Bypass of fix for CVE-2020-26231, Twig sandbox escape"
}
GHSA-FCRP-7GC2-93G7
Vulnerability from github – Published: 2026-07-16 19:14 – Updated: 2026-07-16 19:14Impact
Envoy Gateway accepts extension-managed custom backendRefs from an HTTPRoute to a backend resource in another namespace without requiring a matching Gateway API ReferenceGrant in the target namespace. This breaks the Gateway API cross-namespace consent model: the namespace that owns the referenced backend resource does not need to opt in with a ReferenceGrant before another namespace’s HTTPRoute can use that resource.
Patches
{
  "affected": [
    {
      "package": {
        "ecosystem": "Go",
        "name": "github.com/envoyproxy/gateway"
      },
      "ranges": [
        {
          "events": [
            {
              "introduced": "1.8.0-rc.0"
            },
            {
              "fixed": "1.8.1"
            }
          ],
          "type": "ECOSYSTEM"
        }
      ]
    },
    {
      "package": {
        "ecosystem": "Go",
        "name": "github.com/envoyproxy/gateway"
      },
      "ranges": [
        {
          "events": [
            {
              "introduced": "0"
            },
            {
              "fixed": "1.7.4"
            }
          ],
          "type": "ECOSYSTEM"
        }
      ]
    }
  ],
  "aliases": [
    "CVE-2026-53718"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-862"
    ],
    "github_reviewed": true,
    "github_reviewed_at": "2026-07-16T19:14:50Z",
    "nvd_published_at": null,
    "severity": "MODERATE"
  },
  "details": "### Impact\nEnvoy Gateway accepts extension-managed custom backendRefs from an HTTPRoute to a backend resource in another namespace without requiring a matching Gateway API ReferenceGrant in the target namespace. This breaks the Gateway API cross-namespace consent model: the namespace that owns the referenced backend resource does not need to opt in with a ReferenceGrant before another namespace\u2019s HTTPRoute can use that resource.\n\n### Patches\n[1.7.4](https://github.com/envoyproxy/gateway/releases/tag/v1.7.4)\n[1.8.1](https://github.com/envoyproxy/gateway/releases/tag/v1.8.1)",
  "id": "GHSA-fcrp-7gc2-93g7",
  "modified": "2026-07-16T19:14:50Z",
  "published": "2026-07-16T19:14:50Z",
  "references": [
    {
      "type": "WEB",
      "url": "https://github.com/envoyproxy/gateway/security/advisories/GHSA-fcrp-7gc2-93g7"
    },
    {
      "type": "PACKAGE",
      "url": "https://github.com/envoyproxy/gateway"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:N/AC:H/PR:L/UI:N/S:U/C:H/I:L/A:L",
      "type": "CVSS_V3"
    }
  ],
  "summary": "Envoy Gateway custom backendRef cross-namespace ReferenceGrant bypass"
}
GHSA-FCVM-3W6M-5WPR
Vulnerability from github – Published: 2025-12-05 09:31 – Updated: 2025-12-05 09:31The Payaza plugin for WordPress is vulnerable to unauthorized modification of data due to a missing capability check on the 'wp_ajax_nopriv_update_order_status' AJAX endpoint in all versions up to, and including, 0.3.8. This makes it possible for unauthenticated attackers to update order statuses.
{
  "affected": [],
  "aliases": [
    "CVE-2025-12355"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-862"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2025-12-05T07:16:10Z",
    "severity": "MODERATE"
  },
  "details": "The Payaza plugin for WordPress is vulnerable to unauthorized modification of data due to a missing capability check on the \u0027wp_ajax_nopriv_update_order_status\u0027 AJAX endpoint in all versions up to, and including, 0.3.8. This makes it possible for unauthenticated attackers to update order statuses.",
  "id": "GHSA-fcvm-3w6m-5wpr",
  "modified": "2025-12-05T09:31:07Z",
  "published": "2025-12-05T09:31:07Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2025-12355"
    },
    {
      "type": "WEB",
      "url": "https://wordpress.org/plugins/payaza"
    },
    {
      "type": "WEB",
      "url": "https://www.wordfence.com/threat-intel/vulnerabilities/id/acc88688-76e0-4477-8b7c-eeff541881ab?source=cve"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:L/A:N",
      "type": "CVSS_V3"
    }
  ]
}
GHSA-FCWW-V4HR-RGFR
Vulnerability from github – Published: 2024-01-16 12:30 – Updated: 2025-06-20 21:31Aria Automation contains a Missing Access Control vulnerability.
An authenticated malicious actor may exploit this vulnerability leading to unauthorized access to remote organizations and workflows.
{
  "affected": [],
  "aliases": [
    "CVE-2023-34063"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-862"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2024-01-16T10:15:07Z",
    "severity": "CRITICAL"
  },
  "details": "Aria Automation contains a Missing Access Control vulnerability.\n\n\nAn authenticated malicious actor may \nexploit this vulnerability leading to unauthorized access to remote \norganizations and workflows.",
  "id": "GHSA-fcww-v4hr-rgfr",
  "modified": "2025-06-20T21:31:39Z",
  "published": "2024-01-16T12:30:25Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2023-34063"
    },
    {
      "type": "WEB",
      "url": "https://www.vmware.com/security/advisories/VMSA-2024-0001.html"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:C/C:L/I:H/A:H",
      "type": "CVSS_V3"
    }
  ]
}
GHSA-FCX2-PFMG-PWVQ
Vulnerability from github – Published: 2026-07-05 15:30 – Updated: 2026-07-05 15:30Missing Authorization vulnerability in TUBITAK BILGEM Software Technologies Research Institute Pardus Update allows Privilege Escalation.
This issue affects Pardus Update: from <=0.6.3 before 0.6.6.
{
  "affected": [],
  "aliases": [
    "CVE-2026-6509"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-862"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2026-07-05T15:16:57Z",
    "severity": "HIGH"
  },
  "details": "Missing Authorization vulnerability in TUBITAK BILGEM Software Technologies Research Institute Pardus Update allows Privilege Escalation.\n\nThis issue affects Pardus Update: from \u003c=0.6.3 before 0.6.6.",
  "id": "GHSA-fcx2-pfmg-pwvq",
  "modified": "2026-07-05T15:30:27Z",
  "published": "2026-07-05T15:30:27Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2026-6509"
    },
    {
      "type": "WEB",
      "url": "https://siberguvenlik.gov.tr/guvenlik-bildirimleri/detay/tr-26-0501"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:L/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H",
      "type": "CVSS_V3"
    }
  ]
}
GHSA-FF25-8QM5-3W37
Vulnerability from github – Published: 2025-11-06 18:32 – Updated: 2026-01-20 15:31Missing Authorization vulnerability in CodexThemes TheGem Demo Import (for WPBakery) thegem-importer.This issue affects TheGem Demo Import (for WPBakery): from n/a through <= 5.10.5.
{
  "affected": [],
  "aliases": [
    "CVE-2025-62046"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-862"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2025-11-06T16:16:11Z",
    "severity": "MODERATE"
  },
  "details": "Missing Authorization vulnerability in CodexThemes TheGem Demo Import (for WPBakery) thegem-importer.This issue affects TheGem Demo Import (for WPBakery): from n/a through \u003c= 5.10.5.",
  "id": "GHSA-ff25-8qm5-3w37",
  "modified": "2026-01-20T15:31:54Z",
  "published": "2025-11-06T18:32:56Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2025-62046"
    },
    {
      "type": "WEB",
      "url": "https://patchstack.com/database/Wordpress/Plugin/thegem-importer/vulnerability/wordpress-thegem-demo-import-for-wpbakery-plugin-5-10-5-arbitrary-content-deletion-vulnerability?_s_id=cve"
    },
    {
      "type": "WEB",
      "url": "https://vdp.patchstack.com/database/Wordpress/Plugin/thegem-importer/vulnerability/wordpress-thegem-demo-import-for-wpbakery-plugin-5-10-5-arbitrary-content-deletion-vulnerability"
    },
    {
      "type": "WEB",
      "url": "https://vdp.patchstack.com/database/Wordpress/Plugin/thegem-importer/vulnerability/wordpress-thegem-demo-import-for-wpbakery-plugin-5-10-5-arbitrary-content-deletion-vulnerability?_s_id=cve"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:L/A:N",
      "type": "CVSS_V3"
    }
  ]
}
GHSA-FF29-QR8C-MH26
Vulnerability from github – Published: 2025-12-16 09:31 – Updated: 2026-01-20 15:32Missing Authorization vulnerability in merkulove Grider for Elementor grider-elementor allows Exploiting Incorrectly Configured Access Control Security Levels.This issue affects Grider for Elementor: from n/a through <= 1.0.8.
{
  "affected": [],
  "aliases": [
    "CVE-2025-66161"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-862"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2025-12-16T09:15:58Z",
    "severity": "MODERATE"
  },
  "details": "Missing Authorization vulnerability in merkulove Grider for Elementor grider-elementor allows Exploiting Incorrectly Configured Access Control Security Levels.This issue affects Grider for Elementor: from n/a through \u003c= 1.0.8.",
  "id": "GHSA-ff29-qr8c-mh26",
  "modified": "2026-01-20T15:32:15Z",
  "published": "2025-12-16T09:31:09Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2025-66161"
    },
    {
      "type": "WEB",
      "url": "https://patchstack.com/database/Wordpress/Plugin/grider-elementor/vulnerability/wordpress-grider-for-elementor-plugin-1-0-8-broken-access-control-vulnerability?_s_id=cve"
    },
    {
      "type": "WEB",
      "url": "https://vdp.patchstack.com/database/Wordpress/Plugin/grider-elementor/vulnerability/wordpress-grider-for-elementor-plugin-1-0-8-broken-access-control-vulnerability?_s_id=cve"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:L/A:N",
      "type": "CVSS_V3"
    }
  ]
}
GHSA-FF3J-PX4R-RVXM
Vulnerability from github – Published: 2024-06-09 15:31 – Updated: 2024-06-09 15:31Missing Authorization vulnerability in wpcreativeidea Advanced Testimonial Carousel for Elementor.This issue affects Advanced Testimonial Carousel for Elementor: from n/a through 3.0.0.
{
  "affected": [],
  "aliases": [
    "CVE-2024-32783"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-862"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2024-06-09T13:15:50Z",
    "severity": "MODERATE"
  },
  "details": "Missing Authorization vulnerability in wpcreativeidea Advanced Testimonial Carousel for Elementor.This issue affects Advanced Testimonial Carousel for Elementor: from n/a through 3.0.0.",
  "id": "GHSA-ff3j-px4r-rvxm",
  "modified": "2024-06-09T15:31:09Z",
  "published": "2024-06-09T15:31:09Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2024-32783"
    },
    {
      "type": "WEB",
      "url": "https://patchstack.com/database/vulnerability/advanced-testimonial-carousel-for-elementor/wordpress-advanced-testimonial-carousel-for-elementor-plugin-3-0-0-broken-access-control-vulnerability?_s_id=cve"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:N/I:L/A:N",
      "type": "CVSS_V3"
    }
  ]
}
Mitigation
- Divide the product into anonymous, normal, privileged, and administrative areas. Reduce the attack surface by carefully mapping roles with data and functionality. Use role-based access control (RBAC) [REF-229] to enforce the roles at the appropriate boundaries.
- Note that this approach may not protect against horizontal authorization, i.e., it will not protect a user from attacking others with the same role.
Mitigation
Ensure that access control checks are performed related to the business logic. These checks may be different than the access control checks that are applied to more generic resources such as files, connections, processes, memory, and database records. For example, a database may restrict access for medical records to a specific database user, but each record might only be intended to be accessible to the patient and the patient's doctor [REF-7].
Mitigation MIT-4.4
Strategy: Libraries or Frameworks
- Use a vetted library or framework that does not allow this weakness to occur or provides constructs that make this weakness easier to avoid.
- For example, consider using authorization frameworks such as the JAAS Authorization Framework [REF-233] and the OWASP ESAPI Access Control feature [REF-45].
Mitigation
- For web applications, make sure that the access control mechanism is enforced correctly at the server side on every page. Users should not be able to access any unauthorized functionality or information by simply requesting direct access to that page.
- One way to do this is to ensure that all pages containing sensitive information are not cached, and that all such pages restrict access to requests that are accompanied by an active and authenticated session token associated with a user who has the required permissions to access that page.
Mitigation
Use the access control capabilities of your operating system and server environment and define your access control lists accordingly. Use a "default deny" policy when defining these ACLs.
CAPEC-665: Exploitation of Thunderbolt Protection Flaws
An adversary leverages a firmware weakness within the Thunderbolt protocol, on a computing device to manipulate Thunderbolt controller firmware in order to exploit vulnerabilities in the implementation of authorization and verification schemes within Thunderbolt protection mechanisms. Upon gaining physical access to a target device, the adversary conducts high-level firmware manipulation of the victim Thunderbolt controller SPI (Serial Peripheral Interface) flash, through the use of a SPI Programing device and an external Thunderbolt device, typically as the target device is booting up. If successful, this allows the adversary to modify memory, subvert authentication mechanisms, spoof identities and content, and extract data and memory from the target device. Currently 7 major vulnerabilities exist within Thunderbolt protocol with 9 attack vectors as noted in the Execution Flow.